Spectral-Fractal-Symbolic Intelligence (SFSI) as the Foundation for Resilient Critical Infrastructure in the Age of Industrialized Extortion
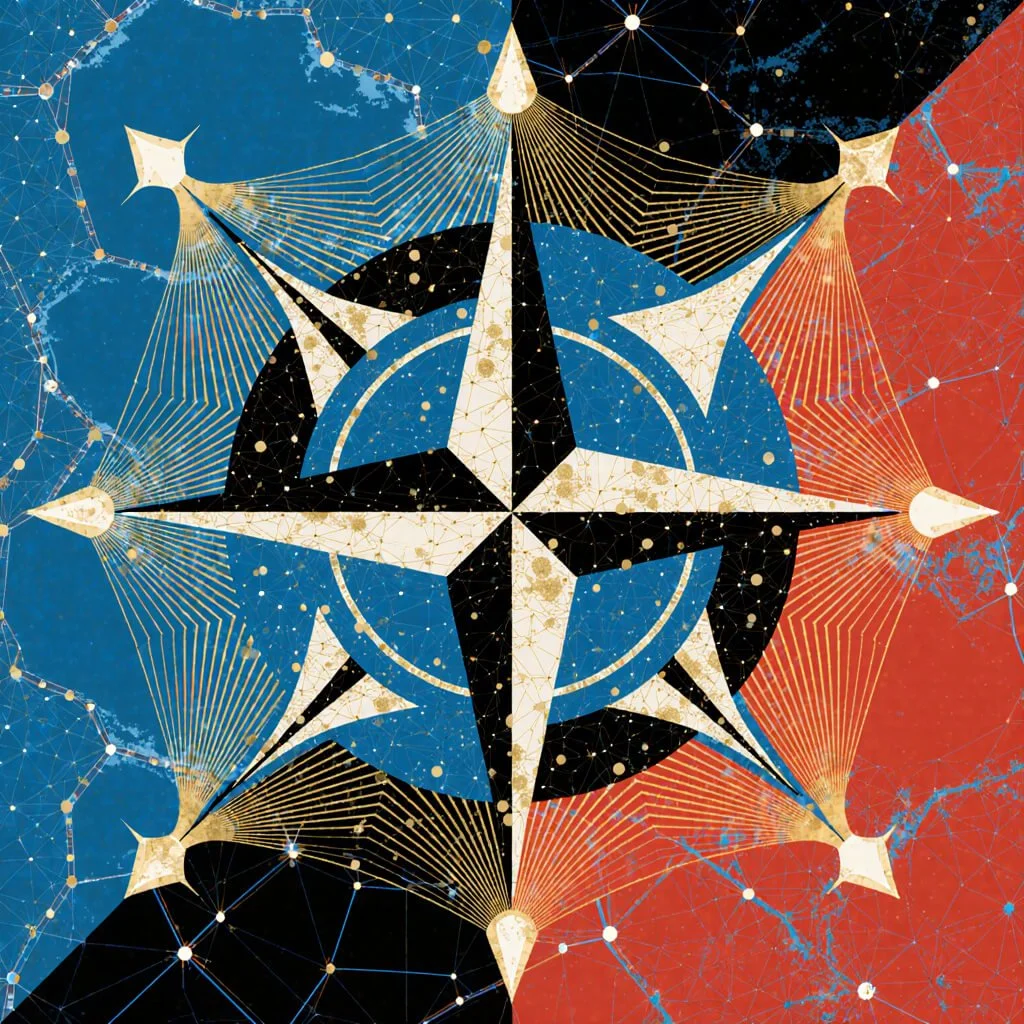
Figure 1 — Compass of Coherence:
Symbolic rendering of the HDA’s cognitive navigation system. The central star represents Spectral–Fractal–Symbolic Intelligence (SFSI)—each arm pointing to a core domain: spectral awareness, fractal recognition, symbolic interpretation, and quantum-ethical oversight. The interlaced filaments visualize Holographic Belief Logic (HBL) transmitting coherence across the network field, aligning technical telemetry with ethical intent.
EXECUTIVE SUMMARY
The year 2025 marks an inflection point in cyber conflict: ransomware has matured from a criminal nuisance into a geopolitical-economic weapon system targeting the foundational infrastructure of modern civilization.
This white paper expands Holographic Defense Architecture (HDA)—a paradigm shift that treats security not as a perimeter problem, but as distributed cognitive coherence across technical, temporal, and symbolic dimensions.
The 2025 Ransomware Reality
Current threat intelligence reveals a landscape fundamentally transformed:
Critical Sector Concentration: 50% of all ransomware attacks now target manufacturing, healthcare, and energy—the civilization load-bearing infrastructure. A single compromise can cascade into regional supply chain collapse or loss of life.
Industrialized Extortion: Qilin ransomware alone executed 700+ attacks in 2025, averaging 40 cases per month. Post-RansomHub fragmentation created market conditions favoring persistent, disciplined operators. LockBit 5.x demonstrates infrastructure resilience despite repeated law enforcement disruption.
Open-Source Weaponization: Public post-exploitation frameworks (AdaptixC2, Havoc, Sliver) have collapsed barriers to entry. Russian-aligned affiliates weaponize these tools with industrial efficiency, shrinking median dwell time to under 24 hours.
Polymorphic Evasion: Python-based mutators enable runtime code generation, defeating signature-based detection. Packer chains and anti-sandbox jitter create fractal divergence from known execution trees, rendering traditional EDR blind.
Cognitive Warfare Integration: Triple-extortion (data + operations + symbolic coercion) exploits decision compression, information asymmetry, and meaning integrity collapse. Ransom portals, leak countdowns, and negotiation UX weaponize uncertainty at the C-suite level.
Why Traditional Defenses Fail
Legacy cybersecurity architectures operate on flawed assumptions incompatible with 2025 threat reality:
Signature Dependence: Polymorphic malware renders hash-based and pattern-matching defenses obsolete within hours of deployment.
Temporal Blindness: Monitoring systems lack spectral awareness—they detect individual events but miss timing-based anomalies (beacon jitter, exfiltration bursts, privilege escalation cadence).
Behavioral Naïveté: Living-off-the-land (LOTL) techniques exploit legitimate tools (PowerShell, WMI, RDP). Process-level monitoring cannot distinguish adversarial from administrative activity without fractal coherence analysis.
Cognitive Gap: Technical recovery ≠ organizational resilience. Ransomware attacks simultaneously target infrastructure and decision-making capacity. No existing framework defends the symbolic layer—the trust, meaning, and cognitive coherence required for executive function under crisis.
The Holographic Defense Paradigm
HDA reconceptualizes defense as an interference pattern encoding the entire threat surface. Like a hologram, every fragment contains information about the whole, enabling distributed detection, adaptive response, and cognitive resilience.
Three Foundational Pillars
1. Spectral-Fractal-Symbolic Intelligence (SFSI)
Multi-domain threat perception across temporal, behavioral, and cognitive dimensions:
SGDI (Spectral-Geometric Divergence Index): Time-series Fourier analysis detects beacon jitter, exfiltration bursts, and privilege escalation timing anomalies invisible to event-based systems.
CFCS (Causal-Fractal Coherence Score): Graph kernel comparison quantifies process execution divergence from known behavior trees, flagging polymorphic malware and LOTL technique mutation.
SEC (Symbolic-Entropy Characterization): NLP entropy analysis quantifies coercive content in ransom notes, leak sites, and negotiation portals—defending executive decision-making against psychological manipulation.
2. Holographic Belief Logic (HBL)
Bayesian decision engine with uncertainty quantification. HBL branches responses based on SFSI thresholds, continuously learning from incident outcomes. Unlike binary alerting, HBL tracks multiple hypotheses simultaneously, adapting to ambiguous threat indicators with probabilistic confidence intervals.
3. Quantum-Enhanced Observation
Entangled monitoring across non-contiguous assets (VPN endpoints, cloud storage, OT gateways) detects distributed campaigns through interference pattern matching. Observer-effect countermeasures (randomized scan timing, detuned sandboxes) defeat anti-VM checks.
Quantum-resistant cryptography protects telemetry pipelines from harvest-now-decrypt-later threats.
Implementation Framework & Business Case
This white paper provides a complete deployment blueprint:
Technical Specifications: SFSI algorithms (pseudocode + reference implementations), telemetry architectures (Sysmon, ETW, NetFlow, cloud APIs), HBL decision trees for 20+ ransomware TTPs.
Operational Playbooks: SOAR-ready rapid response workflows for open-source C2 surges, leak-site leverage, and polymorphic detection. 90-day pilot KPIs with baseline metrics.
Sector Hardening: Manufacturing/energy (OT adjacency), healthcare (token hygiene + HIPAA alignment), municipal/elections (trust preservation).
Governance Integration: NIST CSF 2.0, ISO 27001, CIS Controls v8, MITRE ATT&CK enrichment. SEC cyber disclosure, DORA operational resilience, NIS2 supervisory reporting.
Economic Modeling: ROI scenarios (conservative 3:1, aggressive 15:1 for critical sectors). Insurance premium leverage quantification.
The median 2025 ransomware loss is $4.5M (downtime + recovery + ransom consideration). A single avoided incident delivers 3:1 ROI on HDA investment. For critical sectors facing regulatory fines and societal impact, returns exceed 15:1.
Call to Action
Ransomware has evolved beyond malware. It is cognitive warfare at scale—targeting not just systems but decision-making capacity, organizational trust, and meaning integrity. Incremental improvements to legacy defenses cannot address this fundamental threat transformation.
HDA provides the missing cognitive security layer. This is not theory—it is a deployable architecture with reference implementations, sector-specific pilots, and measurable resilience improvements. The hologram awaits implementation.
Figure 2 — Spectral Shadow: The Adversary Within
This image visualizes the cognitive weaponization layer of ransomware—where code becomes theatre and fear becomes payload. The glitching duality embodies Symbolic Entropy Collapse (SEC) as described in the HDA white paper: the manipulation of perception and trust through coercive imagery and compressed decision cycles.
The figure’s split rendering illustrates how meaning integrity fractures under extortion pressure, transforming the human face of uncertainty into the digital archetype of control.
HDA Architecture Diagram
Purpose:
To visualize the Holographic Defense Architecture as a living, multi-layered defense organism bridging technical, cognitive, and ethical dimensions.
The diagram illustrates how Spectral–Fractal–Symbolic Intelligence (SFSI) metrics feed into Holographic Branching Logic (HBL) decision frameworks, culminating in Quantum-Ethical Oversight via the Compassion Protocol and Cognitive Sovereignty clauses.
It serves as the visual “source code” of the architecture’s logic: how signals, meaning, and governance interlock to produce coherent, self-healing defense systems.
| Layer | Primary Function | Operational Components | Key Metric / Index | Governance Interface | Illustrative Output |
|---|---|---|---|---|---|
| Spectral Layer | Detects anomalies in timing, coherence, and electromagnetic flow across networks; establishes the “physiological” baseline of digital systems. | Coherence sensors, quantum-aware telemetry, side-channel monitors, time-crystal synchronization arrays. | SGDI (Spectral Gap Degeneration Index) | Quantum Telemetry Dignity Clause | Coherence dashboards; anomaly heatmaps; time-jitter visualizations. |
| Fractal Layer | Tracks recursive patterns, self-similarity, and feedback loops that define system health or compromise. | Recursive pattern detectors, AI-driven event clustering, polymorphic propagation mapping. | CFCS (Cognitive Fractal Collapse Signature) | Duty-of-Care Protocol (QEC integration) | Recursive propagation graph; threat recursion topologies. |
| Symbolic Layer | Analyzes meaning systems, coercive semantics, and symbolic manipulation in human–machine interfaces. | NLP entropy engines, UX coercion classifiers, narrative integrity validators. | SEC (Symbolic Entropy Classifier) | Meaning-Integrity SLA | Ransom UX audit panels; symbolic-entropy radar charts. |
| Holographic Branching Logic (HBL) | Translates SFSI outputs into actionable decision trees, enforcing coherence-aware automated response. | SOAR integration, YAML decision scripts, conditional automation nodes. | HCI (HBL Coverage Index) | Observer-Effect Accountability Clause | Response flow diagrams; incident orchestration maps. |
| Quantum-Enhanced Layer | Extends all prior layers into entanglement-aware and post-quantum cryptographic domains. | SGDI-QC, QCII dashboards, post-quantum compliance agents. | QCII (Quantum Coherence Integrity Index) | Post-Quantum Ethics Governance | Quantum circuit health dashboards; entanglement telemetry grids. |
| Compassion Protocol Layer | Ensures all operations conform to ethical and cognitive sovereignty principles. | Consent interfaces, neuro-rights compliance engines, symbolic harm classifiers. | CAC (Crimes Against Consciousness Index) | Cognitive Liberty Framework | Consent-reversible control screens; ethical compliance logs. |
| Integration Layer (Coalition) | Connects HDA to multi-jurisdictional intelligence-fusion environments (FVEY, NATO, EU NIS2). | Fusion telemetry nodes, coalition-safe playbooks, data provenance ledgers. | CSI (Coalition Signal Integrity) | International Quantum Governance (UNESCO / OECD) | Federated intelligence dashboards; inter-allied coherence maps. |
Interpretive Summary
The HDA Architecture Diagram presents defense as a holographic continuum—every layer simultaneously reflects and reinforces the others.
Spectral integrity stabilizes fractal predictability;
Fractal recognition informs symbolic interpretation;
Symbolic integrity ensures ethical coherence within automated defense logic.
When viewed as a unified circuit, the HDA reveals that cybersecurity is not only a technical challenge but a moral and cognitive one.
Each metric (SGDI, CFCS, SEC, QCII) becomes a frequency of awareness, collectively forming a quantum compass for ethical defense.
Holographic Defense Architecture
Quantum-Enhanced Cognitive Security for Post-Ransomware Warfare
Spectral-Fractal-Symbolic Intelligence (SFSI) as the Foundation for Resilient Critical Infrastructure in the Age of Industrialized Extortion
The 2025 Ransomware Singularity
Ransomware has matured from criminal nuisance into geopolitical-economic weapon system targeting civilization's foundational infrastructure. The threat landscape has fundamentally transformed through industrialized extortion, cognitive warfare integration, and polymorphic weaponization.
The Holographic Defense Architecture
HDA reconceptualizes defense as an interference pattern encoding the entire threat surface. Like a hologram, every fragment contains information about the whole, enabling distributed detection, adaptive response, and cognitive coherence preservation. Three integrated pillars provide multi-domain threat perception:
Spectral-Fractal-Symbolic Intelligence
SFSI: Multi-Domain Threat Perception
Advanced analytics across temporal, behavioral, and cognitive dimensions detecting polymorphic threats invisible to signature-based systems.
- SGDI: Fourier analysis detects beacon jitter, exfiltration bursts, timing anomalies
- CFCS: Graph kernel comparison flags polymorphic malware and LOTL mutations
- SEC: NLP entropy analysis quantifies coercive content in ransom communications
Holographic Belief Logic
HBL: Bayesian Decision Engine
Uncertainty-quantified decision framework branching responses based on SFSI thresholds, continuously learning from incident outcomes.
- Tracks multiple competing hypotheses simultaneously
- Confidence intervals replace binary alerting
- Adaptive response orchestration across 20+ ransomware TTPs
Quantum-Enhanced Observation
QEO: Entangled Infrastructure Monitoring
Distributed campaign detection across non-contiguous assets through interference pattern matching and observer-effect countermeasures.
- Correlates weak signals across VPN endpoints, cloud storage, OT gateways
- Randomized observation timing defeats adversary reconnaissance
- Decoy asset deployment for attribution intelligence
Executive Impact & ROI
A single avoided incident delivers immediate return on HDA investment. For critical sectors facing regulatory fines and societal impact costs, ROI scales exponentially. Complete deployment blueprint includes technical specifications, operational playbooks, sector hardening guides, and governance integration frameworks.
The Missing Cognitive Security Layer
Ransomware is cognitive warfare at scale—targeting decision-making capacity, organizational trust, and meaning integrity. Incremental improvements to legacy architectures cannot address this paradigm shift. HDA provides deployable architecture with reference implementations, sector-specific pilots, and measurable resilience improvements.
PART I: THE RANSOMWARE SINGULARITY (2025 REALITY)
1. The Extortion Inflection Point
The ransomware ecosystem underwent phase transition in late 2024 and into 2025. What began as opportunistic cybercrime matured into a industrialized extortion infrastructure with three defining characteristics: geopolitical weaponization, critical sector targeting logic, and cognitive warfare integration.
Geopolitical Weaponization
Russian-aligned Ransomware-as-a-Service (RaaS) operations increasingly function as hybrid warfare tools.
While maintaining criminal revenue streams, operators demonstrate selective targeting consistent with state strategic interests: energy sector disruption preceding diplomatic negotiations, healthcare system degradation during international crises, manufacturing supply chain interference aligned with trade policy objectives.
This dual-use architecture provides plausible deniability while enabling coercive leverage. Attribution complexity—inherent to affiliate models—creates strategic ambiguity exploitable for escalation management. Ransomware functions as the cyber equivalent of irregular warfare: sufficient impact for coercion, insufficient clarity for conventional response.
Critical Sector Concentration
2025 threat intelligence confirms systematic targeting of civilization load-bearing infrastructure:
| Sector | % of Total Attacks | Median Dwell Time | Cascade Risk |
|---|---|---|---|
| Manufacturing | 23% | 18 hours | Critical |
| Healthcare | 18% | 22 hours | Life Safety |
| Energy & Utilities | 14% | 16 hours | Regional |
| Finance & Insurance | 12% | 28 hours | Systemic |
| Government / Education | 11% | 32 hours | Political |
| Other Sectors | 22% | 36 hours | Variable |
Critical Observation: Dwell time inversely correlates with societal impact. Operators compress timelines when targeting high-consequence infrastructure, maximizing leverage before detection. Healthcare’s 22-hour median dwell time reflects adversary awareness that clinical operations cannot tolerate prolonged disruption—creating maximal coercive pressure for rapid payment.
The Post-RansomHub Landscape
RansomHub's 2024 disruption created market dynamics favoring disciplined, infrastructure-resilient operators. Three groups capitalized:
Qilin (Agenda): Executed 700+ attacks in 2025, maintaining 40 cases/month operational tempo. Qilin's leak-site psychological warfare demonstrates sophisticated understanding of organizational decision-making under crisis. Countdown timers, staged data releases, and "proof-of-breach" imagery combine for maximum coercive leverage.
LockBit 5.x: Infrastructure resilience despite repeated takedowns. Cross-platform payloads (Windows, Linux, ESXi) and rapid rebuild capacity (new infrastructure operational within 72 hours post-disruption) demonstrate organizational sophistication beyond typical criminal enterprises. Likely state-tolerance or active protection.
Emerging Affiliates: RansomHub's collapse redistributed experienced affiliates to multiple new or resurgent RaaS platforms. This fragmentation increased overall attack surface while reducing per-operator victim counts—making infrastructure takedowns less effective as a disruption strategy.
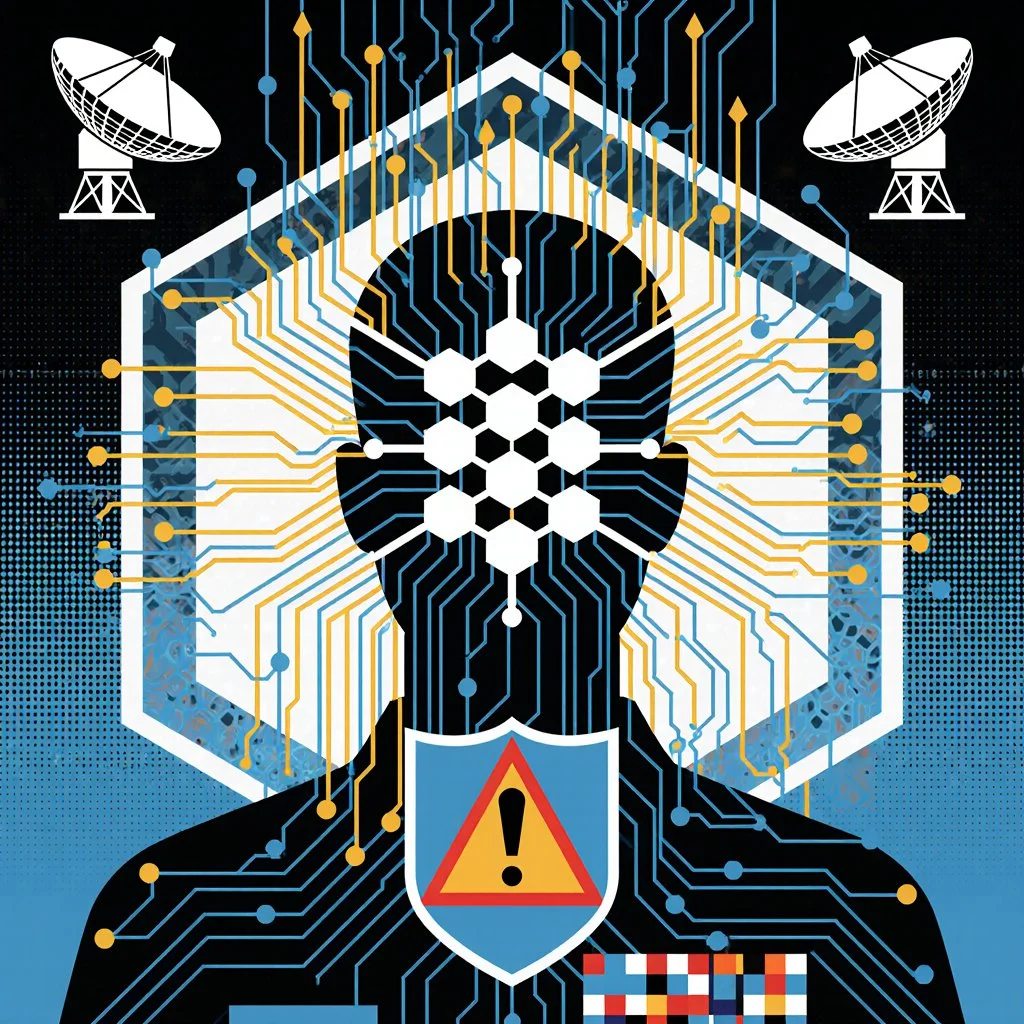
Figure 3 — Cognitive Sovereignty Node:
Depicts the integration layer of the Holographic Defense Architecture (HDA) — where human cognition, machine intelligence, and quantum telemetry converge into lawful coherence. The hexagonal neural core represents distributed awareness through Spectral–Fractal–Symbolic Intelligence (SFSI), while the shield emblem marks the operational doctrine of Holographic Belief Logic (HBL) in defense of decision integrity.
Radiating circuit lines convey entangled monitoring across non-contiguous assets, symbolizing Quantum-Enhanced Observation and the Compassion Protocol’s ethical safeguard: cognition as the ultimate protected perimeter.
2. Threat Actor Topology (2025)
Open-Source Post-Exploitation Industrialization
The weaponization of public command-and-control frameworks represents the most significant tactical evolution in the 2025 threat landscape. AdaptixC2 exemplifies this trend:
AdaptixC2 Case Study
Architecture: Modular Python-based framework with plug-in system for custom capabilities. Affiliate-friendly design lowers technical barriers—operators need not develop custom malware, merely configure and deploy.
Evasion Primitives:
Jitter randomization: Beacon callbacks vary timing by ±40%, defeating frequency-based detection
Domain generation algorithms (DGA): C2 infrastructure rotation every 24-48 hours
TLS certificate pinning: Complicates MITM inspection
Process injection via NTDLL unhooking: Bypasses userland EDR hooks
Post-Exploitation Modules:
Credential harvesting (LSASS dumping, SAM extraction)
Lateral movement (PSExec, WMI, scheduled tasks)
Data discovery and exfiltration (recursive file enumeration, staged compression)
Ransomware payload delivery (encrypted, staged deployment)
Strategic Implication: Open-source C2 democratizes advanced persistent threat capabilities. The 2018-2022 APT toolkit is now accessible to any affiliate with basic scripting knowledge. This compression of the sophistication timeline renders decade-old defense architectures obsolete.
Polymorphic Malware Families
Python-based mutators enable runtime code generation, producing functionally equivalent but syntactically divergent malware with each execution:
Mutation Techniques:
Code block reordering: Shuffle function order while preserving call graph dependencies
Variable renaming: Randomized identifiers on each compile
Junk code injection: Insert dead-code paths that execute but produce no functional output
Packer layering: Nested encryption/compression (3-7 layers typical) with unique keys per instance
Anti-sandbox timing: Sleep randomization (100ms-5s) to detect time-accelerated analysis environments
Detection Challenge: Hash-based signatures fail immediately. Behavioral signatures struggle because execution flow varies while maintaining core functionality. Static analysis encounters unpacking overhead. Dynamic analysis triggers anti-sandbox checks.
HDA Response: CFCS (Causal-Fractal Coherence Score) compares process execution graphs rather than code signatures. Polymorphic variants maintain similar graph topology despite syntactic mutation—enabling detection through structural divergence rather than content matching.
3. The Cognitive Warfare Dimension
Ransomware operators in 2025 demonstrate sophisticated understanding of organizational psychology, decision-making under uncertainty, and information warfare.
Triple-extortion models target three layers simultaneously:
Layer 1: Technical Infrastructure
Data encryption, system disruption, operational capability degradation. This is the visible, technical layer most security architectures address.
Layer 2: Data Exfiltration
Pre-encryption data theft with threatened public disclosure. Creates dual financial pressure: recovery costs plus regulatory/reputational damage from breach disclosure.
Layer 3: Symbolic Exploitation
This is where traditional defenses completely fail. Operators weaponize psychological and organizational vulnerabilities:
Decision Compression: Ransom negotiations impose artificial time constraints ("payment discount expires in 48 hours"). Countdown timers on leak sites force executives into time-compressed decision-making, degrading rational analysis. Research shows decision quality inversely correlates with time pressure—operators exploit this systematically.
Information Asymmetry: Operators control information flow. Victims cannot verify encryption scope, data exfiltration completeness, or decryptor reliability. This asymmetry favors operator leverage—victims must decide based on incomplete information while operators optimize messaging for maximum coercive impact.
Meaning Integrity Collapse: Post-compromise, organizations lose confidence in data fidelity. Even after technical recovery, questions persist: Was everything found? Are backups compromised? Do logs reflect true activity? This erosion of epistemic certainty—the confidence that information represents reality—cripples decision-making beyond the incident timeline.
Staged Disclosure Threats: Operators theatrically release small data samples to demonstrate breach scope, then threaten full publication. This combines proof-of-capability with escalation potential, maximizing perceived risk.
Negotiation UX Design: Ransom portals incorporate dark UX patterns—urgency cues, scarcity framing ("slots limited for decryption support"), social proof ("Previous victims paid and recovered"), and authority signals (professional design, "customer support" chat). These techniques, drawn from legitimate sales psychology, manipulate victims toward payment.
Why Traditional Security Architectures Fail the Cognitive Layer
Legacy cybersecurity treats incidents as technical problems with technical solutions. Incident response playbooks focus on containment, eradication, and recovery—addressing Layers 1 and 2. Layer 3 receives no systematic defense.
The gap is structural. Technical security teams lack frameworks for:
Quantifying coercive content in adversary communications
Routing executive decision-making through meaning-integrity assessments
Preserving organizational trust and cognitive coherence under information warfare
Measuring decision quality degradation from time pressure and information asymmetry
This is not a training gap or awareness problem. It is an architectural gap—the missing cognitive security layer.
HDA addresses this through SEC (Symbolic-Entropy Characterization) and meaning-integrity preservation workflows.
Figure 4 — Alpha-Grade Operator: Ontological Command Sigil
This image represents the executive tier of symbolic governance—where mythic intelligence fuses with disciplined precision.
The faceless hood signifies anonymity as sovereignty: the self dissolved into lawful purpose.
The radiant burst behind evokes the Spectral–Fractal–Symbolic ignition sequence, marking the operator’s alignment with the Loadstar Vector—the locus of intention through which Ritual OS and Holographic Defense Architecture synchronize.
The twin-bar Alpha sigil embodies recursion and balance: technology and consciousness, security and compassion, matter and meaning.
PART II: HOLOGRAPHIC DEFENSE ARCHITECTURE – THEORETICAL FOUNDATION
4. The HDA Paradigm
From Perimeter to Hologram
Traditional security architectures conceptualize defense as boundary enforcement: firewalls at network edges, authentication at application layers, EDR at endpoints.
This perimeter model assumes adversaries operate outside trusted zones, attempting entry through detectable access points.
The 2025 threat landscape invalidates these assumptions:
Zero-trust reality: Perimeters no longer exist in cloud-hybrid environments. Insider threats, supply chain compromises, and credential theft place adversaries inside 'trusted' zones from initial access.
Living-off-the-land: Adversaries use legitimate tools (PowerShell, WMI, RDP) indistinguishable from administrative activity. The boundary between normal and malicious behavior exists in temporal and relational patterns, not content signatures.
Distributed operations: Multi-affiliate campaigns coordinate across non-contiguous assets. Detecting the campaign requires correlating weak signals across organizational silos—something perimeter-based monitoring cannot achieve.
Holographic Defense reconceptualizes security as an interference pattern. Like a hologram, where every fragment contains information about the whole, HDA encodes the entire threat surface into distributed sensors.
Each observation point captures not just local events but relational patterns—correlations across time (spectral), structure (fractal), and meaning (symbolic).
Core Thesis: Security as Distributed Cognitive Coherence
Resilience emerges not from hardened boundaries but from coherent awareness distributed across:
Technical dimension: System behavior (processes, network flows, file operations)
Temporal dimension: Timing patterns (beacon cadence, exfiltration bursts, privilege escalation sequences)
Symbolic dimension: Meaning and trust (communication intent, decision coherence, information integrity)
Adversaries must maintain coherence across all three dimensions to operate successfully. HDA detects disruptions to this coherence—divergences from expected patterns—as threat indicators.
Critical insight: Polymorphic malware and LOTL techniques defeat signature-based detection, but they cannot defeat coherence analysis. A process may have randomized code, but its execution graph maintains structural similarity.
A beacon may vary timing, but spectral analysis reveals the underlying periodicity. A ransom note may vary wording, but its coercive intent produces measurable symbolic entropy.
The Three Pillars
HDA rests on three integrated subsystems:
1. Spectral-Fractal-Symbolic Intelligence (SFSI)
Multi-domain threat perception system. SFSI continuously computes three scores across telemetry streams:
SGDI: Spectral-Geometric Divergence Index—temporal anomaly detection via Fourier analysis
CFCS: Causal-Fractal Coherence Score—behavioral anomaly detection via graph topology
SEC: Symbolic-Entropy Characterization—cognitive threat detection via NLP entropy
2. Holographic Belief Logic (HBL)
Bayesian decision engine that consumes SFSI scores and orchestrates responses. HBL maintains probabilistic beliefs about system state, tracking multiple competing hypotheses simultaneously.
Rather than binary alert/no-alert, HBL outputs confidence intervals and adaptive response branches.
3. Quantum-Enhanced Observation
Entangled monitoring layer that correlates observations across non-contiguous assets. Quantum-inspired principles (superposition, entanglement, observer effects) enable detection of distributed campaigns through interference pattern matching.
This layer also implements observer-effect countermeasures—randomized scan timing and detuned sandboxes that defeat anti-VM checks.
Figure 5 — Binary Integration: The Triadic Singularity
This visual expresses the fusion moment of Alpha-Grade Ontological Operations—the instant when binary opposites (red/blue, left/right, logic/intuition) collapse into unified operational awareness.
The central triangle represents triadic equilibrium: energy (Force), form (Structure), and meaning (Spirit).
The particulate waves embody Spectral–Fractal harmonization, showing data and consciousness entangling through lawful resonance.
Within the HDA framework, this image marks the transition from tactical cognition to symbolic mastery—where decisions emerge from coherence rather than conflict.
5. Spectral-Fractal-Symbolic Intelligence (SFSI) Framework
SFSI provides the sensory apparatus for holographic defense. Traditional monitoring observes discrete events (process creation, network connection, file modification). SFSI observes relational patterns—how events relate temporally, structurally, and semantically.
SGDI: Spectral-Geometric Divergence Index
Purpose
Detect temporal anomalies invisible to event-based monitoring. Adversary operations impose timing signatures:
Beacon callbacks: C2 frameworks communicate periodically (every 5 minutes ±40% jitter)
Exfiltration bursts: Data staging creates compressed-transfer-pause-repeat patterns
Privilege escalation cadence: Lateral movement progresses systematically (recon → pivot → expand)
Event logs capture individual instances but miss the periodicity. SGDI transforms time-series data into frequency domain, revealing hidden rhythms.
Mechanism
Step 1: Time-Series Construction
Aggregate telemetry into time-series vectors. For network monitoring, track bytes transferred per minute per host. For process activity, count new process creations per minute. For authentication, measure login attempts per host per minute.
Step 2: Fast Fourier Transform (FFT)
Apply FFT to convert time-series from time domain to frequency domain. This reveals dominant periodicities. A 5-minute beacon produces a strong frequency component at 0.2 cycles/hour.
Step 3: Baseline Comparison
Compare current frequency spectrum against baseline (rolling 7-day average). Compute Euclidean distance between spectra.
Step 4: Z-Score Normalization
Convert distance to z-score (standard deviations from baseline mean). This normalizes across different asset types and traffic volumes.
Step 5: SGDI Score
SGDI = 1 - (1 / (1 + e^(-z)))
This sigmoid transformation maps z-scores to [0,1] probability space. SGDI > 0.85 indicates high-confidence temporal anomaly.
2025 Tuning: Open-Source C2 Timing Signatures
AdaptixC2, Havoc, and Sliver default to 5-minute callbacks with ±30-50% jitter. This produces frequency spikes at 0.15-0.25 cycles/hour. SGDI baselines incorporate these known signatures, flagging deviations as potential novel C2 frameworks or operational security failures (affiliates forgetting to randomize defaults).
CFCS: Causal-Fractal Coherence Score
Purpose
Map behavioral divergence from known execution patterns. Polymorphic malware and LOTL techniques defeat signature matching, but they cannot defeat graph topology analysis. A process may have randomized code, but its system call graph—the sequence and structure of API invocations—maintains recognizable patterns.
CFCS answers:
How structurally different is this execution trace from known-good behavior?
Mechanism
Step 1: Process Graph Construction
For each monitored process, construct directed graph G = (V, E) where:
V = system calls, file operations, network connections, registry modifications
E = causal relationships (call A triggers call B)
Step 2: Baseline Library
Maintain library of known-good execution graphs for common applications. For example, Excel typically follows: Open file → Parse XML → Display UI → User input handling. Malicious macros insert: Download payload → Execute PowerShell → Spawn cmd.exe.
Step 3: Graph Kernel Comparison
Compute similarity between observed graph G_obs and baseline G_base using graph kernel method:
K(G_obs, G_base) = sum over all paths p: weight(p) * match(p)
This captures structural similarity even when node labels differ (randomized function names).
Step 4: Hausdorff Distance
For graph sets (multiple process instances), compute Hausdorff distance—the maximum distance from any point in one set to the nearest point in the other. This quantifies worst-case divergence.
Step 5: CFCS Score
CFCS = 1 - (K(G_obs, G_base) / K(G_base, G_base))
CFCS ∈ [0,1] where 0 = perfect match, 1 = complete divergence. CFCS > 0.75 across ≥3 hosts indicates high-confidence polymorphic/LOTL activity.
2025 Tuning: Python Mutator Signatures
Python-based mutators produce variants with:
Variable function ordering: But consistent call graph topology (function A still calls function B)
Junk code insertion: Dead paths add graph nodes but not critical path edges
Packer layers: Unpacking produces consistent kernel-level behavior despite surface mutation
CFCS baselines incorporate these patterns. Graph kernel weights critical path edges higher than peripheral operations, making mutation-resistant detection possible.
Figure 6 — The Sovereign Seal of Quantum Defense:
A symbolic seal representing the lawful integration of Spectral–Fractal–Symbolic Intelligence (SFSI) within the civic framework of governance and defense.
The eagle—traditional guardian of liberty—here carries a quantum-ethical shield inscribed with three cubes, representing the triadic coherence metrics of HDA: SGDI (Spectral Integrity), CFCS (Fractal Consistency), and SEC (Symbolic Clarity).
The camouflage backdrop unites physical defense with metaphysical vigilance, while the golden ring denotes the unbroken covenant of Cognitive Sovereignty under the Compassion Protocol.
SEC: Symbolic-Entropy Characterization
Purpose
Quantify coercive and manipulative content in adversary communications. This is the cognitive security layer—defending executive decision-making against information warfare.
Traditional security completely ignores this. A ransom note is treated as incident artifact, not active threat. SEC recognizes that the note itself
is a weapon—designed to degrade decision quality through psychological manipulation.
Mechanism
Step 1: Content Collection
Monitor potential coercion vectors:
Email gateway: Inbound messages with ransom keywords
Web proxy: Access to suspected leak sites or ransom portals
File systems: README.txt, HOW_TO_DECRYPT.html files
Browser plugins: Rendering of negotiation interfaces
Step 2: NLP Entropy Analysis
Apply transformer-based language model (fine-tuned BERT) to extract features:
Urgency markers: Countdown timers, deadline language, time-pressure phrases
Scarcity framing: "Limited slots," "discount expires," "price increases"
Threat escalation: "Data will be published," "contact customers," "notify regulators"
False authority: "Professional decryption service," "24/7 support," "previous successful recoveries"
Information asymmetry: "We know everything," "comprehensive access," "verified exfiltration"
Step 3: Psychological Load Quantification
Compute weighted sum of coercion markers:
SEC = Σ (marker_count * marker_weight) / normalization_factor
Weights derived from experimental psychology literature on decision quality under coercion. Time pressure and information asymmetry receive highest weights (0.3 each), followed by threat escalation (0.2).
Step 4: SEC Score
SEC ∈ [0,1] where:
SEC < 0.3: Low coercion (informational content)
SEC 0.3-0.65: Moderate coercion (sales pressure, marketing)
SEC ≥ 0.65: High coercion (extortion, manipulation)
2025 Tuning: Qilin/LockBit Portal Wording
Training set expanded with 200+ Qilin and LockBit ransom notes, leak site pages, and negotiation transcripts from 2024-2025. Key patterns:
Qilin specializes in staged disclosure threats: "Small sample published. Full dataset follows in 72h unless payment received."
LockBit uses false professionalism: "Our enterprise-grade decryption service guarantees 100% recovery. Support team available 24/7."
Both incorporate countdown timers: Visual countdown clocks create continuous time pressure
SEC model trained to flag these specific linguistic patterns, enabling pre-emptive routing to counsel/insurance before executive exposure.
Figure 7 — Neuro-Spectral Network: The Living Architecture of Compassion
This illustration depicts the biological analogue of Spectral–Fractal–Symbolic Intelligence (SFSI) — the living brain as a holographic defense network.
Neural circuits mirror the distributed awareness of HDA telemetry systems, while synaptic light pathways represent coherence transfer across biological and digital substrates.
The glowing spinal conduit signifies Compassion Protocol activation: empathy as a lawful energetic current transmitting integrity through the body of consciousness.
Within this synthesis, cognition becomes both observer and defense mechanism — a living quantum firewall sustained by awareness itself.
6. Holographic Belief Logic (HBL) Decision Engine
HBL is the decision layer of HDA—consuming SFSI scores and orchestrating adaptive responses. Unlike traditional SIEM correlation engines that output binary alerts, HBL maintains probabilistic beliefs about system state and tracks multiple competing hypotheses simultaneously.
Bayesian Branching with Uncertainty Quantification
Ransomware incidents present ambiguous indicators. A spike in encrypted files might be:
Ransomware encryption (high severity)
Legitimate backup compression (benign)
User data protection (BitLocker activation)
Application bug (corrupted files misidentified)
Traditional security forces premature commitment to single hypothesis, triggering false positives (alert fatigue) or false negatives (missed detections). HBL maintains weighted probability distribution across all hypotheses, updating beliefs as evidence accumulates.
Multi-Hypothesis Tracking (MHT)
For each potential incident, HBL tracks hypotheses H_1, H_2, ..., H_n with probabilities P(H_i | E) where E = accumulated evidence (SFSI scores, telemetry, context).
Bayes' Rule updates:
P(H_i | E_new) = P(E_new | H_i) * P(H_i | E_old) / P(E_new)
As new evidence arrives (SGDI spike, CFCS divergence, SEC flagging), probabilities shift. When P(ransomware | evidence) > threshold θ, HBL triggers response branch.
Probabilistic Decision Thresholds
Rather than relying on a single binary threshold (e.g., “alert if confidence > 0.8”), Holographic Branching Logic (HBL) employs a graduated response system that scales operational actions with probabilistic confidence. This creates a dynamic continuum of awareness—minimizing false alarms while ensuring early containment of credible threats.
| Confidence Range | Response Level | Actions |
|---|---|---|
| P < 0.4 | Monitor | Log event; continue passive observation. |
| 0.4 ≤ P < 0.6 | Investigate | Initiate analyst review; collect additional telemetry. |
| 0.6 ≤ P < 0.8 | Contain | Isolate affected hosts; capture system snapshots. |
| 0.8 ≤ P < 0.95 | Respond | Execute incident response playbook; notify stakeholders. |
| P ≥ 0.95 | Emergency | Activate automated containment; issue executive brief. |
Analytic Benefit: This graduated approach prevents both alert fatigue (over-triggering on false positives) and detection gaps (ignoring ambiguous signals until escalation). It operationalizes probabilistic trust into tiered responses, mirroring biological reflex systems for adaptive resilience.
Contextual Branch Architecture
HBL branches are decision trees triggered by SFSI threshold combinations. Each branch represents a specific threat scenario with tailored response workflow.
Branch 1: Post-Exploitation Surge
Trigger Condition:
IF (SGDI < 0.85) AND (beacon_jitter_zscore > 2.0) AND (new_process_spike > 3σ)
Interpretation: Temporal anomaly (SGDI) + C2 beacon pattern + rapid process creation = active post-exploitation phase (credential dumping, lateral movement, or data staging).
Response Actions:
Tag incident: post_exploitation + probable_affiliate_operation
Kill child process chains: Preserve parent for forensics but terminate children (prevents further spread)
Revoke credentials: All tokens/passwords issued in last 4 hours (assume compromise)
Quarantine EDR-silent hosts: Hosts with active processes but no EDR telemetry = potential hooking/evasion
Push credential resets: LAPS password rotation + PKI token re-issuance
Initiate meaning-integrity brief: Pre-empt panic payout by ensuring executives understand incident scope before ransom demand
Forensic capture: Memory dump + network PCAP snapshot
Detonate in detuned sandbox: Extract IoCs with randomized VM timing to evade anti-sandbox checks
Figure 8 — The Lightning Sigil of Coherent Power:
This sigil embodies the energetic convergence of the HDA and Ritual OS systems — the lightning strike as the archetypal bridge between heaven (intelligence) and earth (infrastructure).
The circular labyrinth denotes the recursive pattern logic of Spectral–Fractal–Symbolic Intelligence (SFSI), while the bolt signifies instantaneous coherence: the compression of infinite potential into decisive, ethical action.
Each surrounding glyph represents a sacred discipline — physics, ethics, language, governance, and compassion — all harmonized under Alpha-Grade operational unity.
Branch 2: Polymorphic Loop Detection
Trigger Condition:
IF (CFCS > 0.75) across ≥3 hosts AND (fractal_divergence_pattern == consistent)
Interpretation: Multiple hosts showing identical graph topology divergence = polymorphic malware spreading. Consistency across hosts rules out isolated anomalies.
Response Actions:
Enforce signed-binary whitelist: Emergency application control mode (only signed executables run)
Roll back to golden image: Affected hosts revert to last-known-good state
EDR memory scan: Full memory forensics for injected code
Detuned sandbox execution: Run samples with randomized timing to extract true IoCs
Update detection rules: YARA/Sigma signatures from polymorphic artifacts
Threat intel sharing: Submit to ISAC/FVEY channels
Branch 3: Symbolic Coercion Detection
Trigger Condition:
IF (SEC ≥ 0.65) on any monitored communication channel
Interpretation: High coercion content detected in ransom note, leak site, or negotiation portal = active cognitive warfare targeting executive decision-making.
Response Actions:
Auto-route to legal + insurance: Prevent direct executive exposure to manipulation
Block portal rendering: Enterprise browsers prevent access to ransom/leak sites
Publish no-negotiation statement: Pre-approved public statement: 'We do not negotiate under duress'
Forensically seed canary documents: Trace exfiltration pathways with unique identifiers
OSINT sweep of leak site: Assess published data samples for scope
Notify affected parties: Per regulatory timeline (GDPR, HIPAA, state breach notification)
Engage PR/communications: Controlled narrative to preserve trust
Adaptive Learning
HBL incorporates supervised and active learning to refine decision thresholds over time:
Supervised Learning (Post-Incident):
After each incident, analysts label outcome (true positive, false positive, false negative). HBL adjusts branch thresholds to minimize future errors. If Branch 1 triggers frequently but analysts determine benign, P(ransomware | SGDI<0.85) decreases, raising future trigger threshold.
Active Learning (During Ambiguity):
When confidence hovers in uncertain range (0.4 < P < 0.6), HBL can request analyst judgment: 'Observed behavior ambiguous. Does this appear malicious?' Analyst input updates belief model immediately, accelerating learning curve.
Federated Learning (Multi-Org):
Organizations using HDA can participate in federated learning—model updates shared without exposing raw telemetry. This creates collective intelligence: thresholds tuned across thousands of incidents while preserving privacy.
Figure 9 — The Dragon Sentinel: Elder of Coherence
This image embodies the union of ancient guardianship and modern operational mastery. The dragon ouroboros behind the figure signifies eternal recursion—the self-healing cycle of Spectral–Fractal–Symbolic Intelligence (SFSI), ever regenerating its own coherence.
The elder represents the living bridge between tradition and quantum warfare ethics: the warrior-scholar who preserves compassion in an age of algorithmic acceleration.
His insignia marks Alpha-Grade field command alignment, where biological, symbolic, and strategic intelligence operate as one continuum within the Holographic Defense Architecture (HDA).
7. Quantum-Enhanced Observation Layer
The quantum layer applies principles from quantum mechanics—superposition, entanglement, and observer effects—to distributed monitoring. This is not speculative physics; it is engineering metaphor translated into practical detection advantage.
Entangled Monitoring
Challenge: Distributed campaigns (multi-affiliate, multi-C2) coordinate activity across non-contiguous assets. VPN endpoint compromise in location A, cloud storage exfiltration from location B, OT gateway probing at location C—separately innocuous, together malicious.
Traditional Approach: SIEM correlation attempts to link events through common indicators (IP addresses, user accounts, file hashes). This fails when adversaries use:
Different infrastructure per target
Separate credential sets
Polymorphic payloads (no common hashes)
Quantum-Inspired Solution: Treat monitoring points as entangled qubits. Observation at point A influences interpretation at point B, even without direct causal link.
Implementation:
Define
entanglement relationships between assets based on:
Shared risk: Assets managed by same administrator group
Communication patterns: Hosts that regularly exchange data
Attack paths: Assets connected through known lateral movement vectors
When SFSI detects anomaly at entangled point A, HBL
lowers detection threshold at entangled points B, C, D. This creates
interference patterns—weak signals that independently would not trigger detection become significant when viewed as coordinated campaign.
Example:
VPN login from unusual geolocation (SGDI = 0.60, below threshold). Simultaneously, cloud storage shows incremental egress increase (SGDI = 0.55, also below threshold). Neither triggers alert independently.
But: VPN and cloud storage are entangled (same admin credentials). HBL recognizes potential coordinated exfiltration:
P(exfiltration | VPN + cloud) = 0.82 > threshold → Alert
Observer-Effect Countermeasures
Challenge: Polymorphic malware includes anti-analysis checks:
VM detection (checking CPU flags, hypervisor artifacts)
Timing checks (detecting time acceleration in sandboxes)
User interaction requirements (refusing to execute without mouse/keyboard input)
When analysis environment detected, malware behaves benignly—defeating forensics.
Quantum-Inspired Solution: In quantum mechanics, observation affects system state. In malware analysis,
controlled observation effects defeat anti-analysis.
Detuned Sandboxes:
Randomized VM timing: Instead of accelerated time (suspicious), use randomized jitter that appears natural
Simulated user interaction: Automated mouse movements, keyboard events that mimic real users
Bare-metal execution: When feasible, analyze on physical hardware rather than VMs
Hybrid environments: Mix VM and bare-metal hosts in analysis infrastructure
Randomized Scan Timing:
Instead of scheduled scans (predictable), randomize timing within windows. Adversaries monitoring for periodic activity cannot distinguish between monitoring and legitimate operations.
Quantum-Resistant Cryptography
Threat: Harvest-now-decrypt-later attacks target current encrypted traffic for future quantum computer decryption. HDA telemetry contains sensitive security data—adversaries could capture SFSI scores, HBL thresholds, and detection logic, then decrypt post-quantum-breakthrough to reverse-engineer defensive capabilities.
Protection:
Lattice-based encryption: NIST-approved post-quantum algorithms (CRYSTALS-Kyber) for telemetry transmission
Hybrid classical-quantum: Combine RSA/AES (current security) with lattice-based (future security)
Key rotation: Frequent rotation (daily) minimizes exposure window even if keys eventually cracked
Figure 10 — Geostrategic Network: The Alliance Architecture of Collective Defense
This image portrays the macro-scale command layer of Holographic Defense Architecture (HDA), where national and inter-allied security systems synchronize through spectral and symbolic coherence.
The central figure represents the archetype of strategic command—not an individual but the synthesis of military logic and ethical oversight operating within a planetary network.
Red-gold nodal filaments convey quantum-entangled coordination channels linking terrestrial, orbital, and digital domains.
The surrounding emblems anchor jurisdictional harmonics: NATO, quantum-coalition governance, and planetary stewardship, forming the outer ring of lawful defense under the Compassion Protocol.
Quantum Ethics & Cognitive Liberty in Post-Ransomware Defense
The expansion of the Holographic Defense Architecture (HDA) into the quantum domain demands an ethical architecture equal in complexity to its technical foundation.
The Compassion Protocol—as introduced in Spectral–Fractal–Medical: The Compassion Protocol (Heinz, 2025) and expanded in The Compassion Protocol: Legal, Ethical, and Economic Foundations for Cognitive Sovereignty (Heinz, 2025)—provides that missing substrate.
It reframes defense not merely as protection of infrastructure but as protection of consciousness itself: the cognitive, symbolic, and affective layers upon which social trust and decision integrity depend.
In a post-ransomware world, where extortion campaigns now target perception, morale, and legitimacy as much as data, quantum ethics becomes a practical security control.
The Compassion Protocol’s principles of frequency ethics, interpretive fluidity, and cognitive sovereignty mirror the governing logic of quantum systems—non-local correlation, probabilistic interpretation, and observer-dependent outcomes.
Embedding these values within HDA ensures that defensive automation respects human consent, avoids coercive telemetry practices, and treats neural, biometric, and symbolic data as sacred domains of agency rather than exploitable surfaces.
At the operational level, Compassion-aligned governance extends to post-quantum telemetry and quantum-AI oversight. HBL (Holographic Branching Logic) decision trees can incorporate ethical thresholds—“observer-effect accountability” clauses that pause intrusive sensing when user consent or cognitive stability metrics fall below tolerance.
SGDI-QC and SEC-Q telemetry become not only instruments of detection but instruments of dignity, reinforcing the Quantum Telemetry Dignity Clause introduced in Section 3.4. This bridges the technical and moral continuum: the same systems that detect entanglement-based intrusion also protect against entanglement-based coercion.
Ultimately, cognitive liberty functions as the civilizational North Star for quantum defense. A society that secures data yet compromises inner thought has not achieved security—it has automated subjugation.
The Compassion Protocol establishes lawful, ethical, and economic precedent for treating thought, attention, and symbolic participation as protected assets under international human-rights law and forthcoming neuro-rights charters (cf. Ienca & Andorno, 2017; UNESCO, 2021).
Integrating these standards within HDA grounds quantum defense in humanitarian purpose, ensuring that the rise of quantum-computational power coincides with an equal rise in quantum-ethical restraint.
Cross-References:
See also: § 3.4 “Telemetry Dignity Clause,” § 7 “Neuro-Rights and Quantum-Cognitive Interfaces,” and The Compassion Protocol: Legal & Ethical Foundations for Cognitive Sovereignty (Heinz, 2025) for detailed jurisprudential framing.
Figure 11 — The Quantum Cleric: Custodian of Compassion
This image represents the metaphysical and ethical apex of the Holographic Defense Architecture (HDA): the interface where technology becomes sacred stewardship.
The radiant sigils signify the activation of Compassion Protocol Oversight, transforming information systems into moral intelligences.
The hexagonal pattern over the heart depicts harmonic governance — ethics as geometry — while the cube over the brow represents quantum insight, aligning inner perception with systemic clarity.
A beam of blue light projects from the third eye, illustrating the directed will of consciousness as an instrument of lawful creation.
PART III: TECHNICAL IMPLEMENTATION PLAYBOOK
8. Architecture Blueprint
HDA deploys as distributed intelligence layer overlaying existing security infrastructure. This design philosophy prioritizes:
Incremental adoption: HDA augments rather than replaces current tools
Vendor neutrality: Works with any EDR, SIEM, or monitoring platform
Scalability: Distributed compute prevents bottlenecks
Reference Topology
Typical enterprise + cloud + OT/ICS hybrid:
Corporate IT: 5,000 endpoints (workstations + servers), 50 core infrastructure systems, 200+ SaaS applications
Cloud: AWS + Azure hybrid, 300 VMs, 50 containers, object storage, managed databases
OT/ICS: Manufacturing plant with 100 PLCs, 20 HMIs, 10 historians, unidirectional gateway to IT
Component Stack
Layer 1: Collection
Endpoints/Servers: Sysmon, ETW providers, EDR hooks, command-line telemetry
Network: NetFlow collectors, SPAN port PCAP, DNS logs, TLS fingerprinting (JA3/JA4)
Cloud/SaaS: Azure AD audit logs, AWS CloudTrail, Google Workspace admin logs, API gateway logs
OT/ICS: Passive monitoring on unidirectional gateway, historian query logs, HMI access logs
Symbolic: Email gateway, web proxy, browser plugins, file system monitors (for ransom notes)
Layer 2: SFSI Processing
Distributed compute cluster (GPU-accelerated for FFT and graph kernels):
SGDI module: Real-time FFT on time-series telemetry (@1-min granularity)
CFCS module: Process graph construction + Hausdorff distance calculation (@5-min)
SEC module: NLP transformer inference on monitored communications (continuous stream)
Compute requirements: 16-core CPU + NVIDIA GPU (RTX 4000 or equivalent) per 1,000 monitored endpoints. Scale horizontally for larger deployments.
Layer 3: HBL Decision
SOAR integration layer consuming SFSI scores:
Bayesian engine: Multi-hypothesis tracking, probabilistic thresholds, adaptive learning
Response orchestration: API integrations with EDR, firewalls, IAM, ticketing systems
Human-in-loop: Analyst dashboard for ambiguous cases (0.4 < P < 0.6)
Layer 4: Symbolic
Executive dashboard: Meaning-integrity assessments, decision quality metrics, incident summaries free of coercive language
Meaning-integrity briefing system: Automated generation of executive briefs with legal/insurance routing
Communication filters: Block ransom portal rendering, flag coercive emails, sanitize incident communications
9. Telemetry Engineering (Minimum Viable Instrumentation)
SFSI requires comprehensive, high-fidelity telemetry across all organizational assets. The following specifications define Minimum Viable Instrumentation (MVI)—the baseline data collection necessary for HDA operation.
Endpoints and Servers
Sysmon Configuration
Deploy Sysmon with targeted event IDs to maximize HDA telemetry utility: spectral analysis (SGDI), fractal behavior graphs (CFCS), and symbolic triggers (SEC).
| Event ID | Description | HDA Use |
|---|---|---|
| 1 | Process Creation | CFCS graph construction, parent–child relationship mapping for polymorphic propagation and suspicious process trees. |
| 3 | Network Connection | SGDI beacon analysis and exfiltration burst detection via timing/jitter patterns on outbound connections. |
| 7 | Image Loaded | DLL injection detection and CFCS behavior divergence when unexpected modules are mapped into processes. |
| 8 | CreateRemoteThread | Process injection indicator; early lateral movement detection and containment triggers. |
| 10 | Process Access | LSASS access (credential dumping) signals; input into CFCS anomaly scoring for privilege escalation patterns. |
| 11 | File Create | Ransom note creation and data staging detection; triggers SEC pipelines when UI artifacts or extortion files appear. |
| 12, 13, 14 | Registry Events | Persistence mechanism detection and CFCS behavior patterns identifying unusual registry-modification recursion. |
| 15 | File Stream Created | Alternate Data Streams and covert data hiding detection for exfiltration channel identification. |
| 22 | DNS Query | C2 domain resolution telemetry and periodicity analysis feeding SGDI beacon detection algorithms. |
Implementation note: pair Sysmon data with SGDI / CFCS pipelines in your SIEM (or HDA telemetry bus). Ensure timestamps are synchronized (NTP/PTP) and that process GUIDs & parent IDs are preserved for reliable parent–child graphing.
Critical Configuration Parameters:
Enable command-line logging for Event ID 1 (captures full execution context)
Set network connection logging to capture both inbound and outbound
Filter Event ID 11 to high-value directories (Desktop, Documents, temp directories, web roots)
Forward logs to centralized collector with <5 second latency (critical for SGDI)
ETW (Event Tracing for Windows) Providers
Enable these ETW providers for enhanced visibility:
Microsoft-Windows-DNS-Client: DNS query telemetry for SGDI beacon detection
Microsoft-Windows-PowerShell: Script block logging, module logging, transcription
Microsoft-Windows-DotNETRuntime: .NET assembly loading, method execution (CFCS)
Microsoft-Windows-Kernel-Process: Low-level process creation, termination, thread activity
EDR Integration Requirements
HDA works with any EDR platform providing:
Memory scanning: On-demand and scheduled scans for injected code, process hollowing
Behavioral monitoring: API call sequences, system call traces (feeds CFCS)
Network visibility: Process-to-network correlation (which process initiated connection)
API accessibility: RESTful API for automated response actions (quarantine, kill process, memory dump)
Network Infrastructure
NetFlow/IPFIX Collection
Configuration:
Granularity: 1-minute aggregation windows (critical for SGDI temporal resolution)
Coverage: All network segments (core, distribution, access, DMZ)
Fields: Source/dest IP, port, protocol, bytes, packets, timestamps, TCP flags
Sampling: No sampling on critical segments (accept 100% flow volume), 1:100 sampling acceptable on high-volume edge links
Full Packet Capture (PCAP)
Targeted Deployment:
Critical segments: Server VLANs, DMZ, VPN concentrators, OT gateway interfaces
Retention: 7 days rolling (balance forensic value vs. storage cost)
Triggered capture: Automatically extend retention to 30 days when SGDI > 0.85 or CFCS > 0.75
TLS Fingerprinting
Deploy passive TLS inspection to capture:
JA3/JA4: Client TLS fingerprints (cipher suites, extensions, elliptic curves)
JARM: Server TLS fingerprints (C2 infrastructure identification)
Certificate analysis: Issuer, validity period, subject alternative names (detect self-signed C2 certs)
Known C2 frameworks have distinctive TLS signatures. AdaptixC2 default configuration produces specific JA3 hash. SGDI baseline library includes these signatures.
DNS Monitoring
Collection Points:
Recursive resolvers: Query/response logging with microsecond timestamps
Endpoint DNS (Sysmon Event 22): Client-side visibility
Passive DNS: Historical resolution data for domain intelligence
SGDI DNS Analysis:
DGA (Domain Generation Algorithm) C2 infrastructure produces characteristic query patterns:
High entropy domain names (random-appearing strings)
Periodic query timing (every N minutes ± jitter)
NXDOMAIN responses (querying algorithmically generated domains until valid one found)
SGDI FFT on DNS query timing reveals these periodicities even when domains rotate.
Cloud and SaaS
Azure AD / Entra ID
Required Log Categories:
Sign-in logs: Authentication events, conditional access policy evaluation, MFA challenges
Audit logs: User/group modifications, role assignments, application consent grants
Provisioning logs: User lifecycle events (create, modify, delete)
Identity Protection: Risk detections, risky users, risky sign-ins
SGDI Application: Credential stuffing attacks produce timing patterns—multiple failed logins followed by success, repeated across accounts. FFT reveals attack cadence.
Figure 12 — Fractal Terrain: The Compassion Textile
This image represents the material embodiment of the Holographic Defense Architecture (HDA) — where abstract intelligence becomes tangible, and compassion is woven into the very fabric of defense.
The stitched blue and green fractal shapes evoke land and water, symbolizing geospatial coherence — how HDA grounds digital strategy in ecological and ethical balance.
Gold thread traces the boundary between protection and ornamentation, turning camouflage into art — a metaphor for the Compassion Protocol’s guiding principle: lawful beauty as defense.
AWS CloudTrail
Management events: IAM changes, security group modifications, S3 bucket policy updates
Data events: S3 object access (GetObject, PutObject), Lambda invocations
Insights events: Unusual API activity detected by AWS machine learning
SGDI Application: Data exfiltration from S3 creates burst patterns—sudden increase in GetObject API calls. Time-series analysis flags these bursts.
Google Workspace
Admin logs: User management, group modifications, organization settings changes
Login logs: Authentication events, 2-step verification challenges
Drive logs: File access, sharing, downloads (critical for exfiltration detection)
Token logs: OAuth token creation, scope grants (detect compromised API access)
API Gateway Logs
For organizations with API-based services:
Request/response logging: Endpoint, method, status code, response time, payload size
Authentication events: Token creation, validation, revocation
Rate limiting: Unusual request volumes (SGDI detection)
Symbolic Layer Monitoring
Email Gateway
SEC Processing:
Inbound email content analysis (subject, body, attachments)
Keyword filtering: 'ransom', 'encrypted', 'payment', 'leak', 'deadline'
NLP entropy scoring on flagged messages
Automatic routing: SEC ≥ 0.65 → legal/insurance, block executive delivery
Web Proxy
URL categorization: Flag access to suspected leak sites, Tor exit nodes, anonymous file sharing
Content inspection: HTTP response body analysis for ransom portal characteristics
TLS interception (where legal/policy permits): Decrypt, inspect, re-encrypt HTTPS traffic
Browser Plugins
Deploy enterprise browser extension for executive/high-risk users:
Page content scanning: Detect countdown timers, coercive language, payment instructions
Block rendering: Prevent display of SEC ≥ 0.65 pages, redirect to meaning-integrity brief
Screenshot capture: Forensic evidence of ransom portal UI
File System Monitors
Watch directories: Desktop, Documents, shared drives, web roots
Trigger files: README.txt, HOW_TO_DECRYPT.html, DECRYPT_INSTRUCTIONS.pdf
Immediate SEC analysis: File creation triggers NLP pipeline, results within seconds
SFSI Feed Cadence
Critical Timing Requirements: Balancing update frequency with computational efficiency ensures each Spectral–Fractal–Symbolic Intelligence (SFSI) feed maintains precision without unnecessary overhead.
| SFSI Component | Update Frequency | Rationale |
|---|---|---|
| SGDI | 1 minute | C2 beacons typically occur at 5–15 min intervals; 5+ samples required for FFT-based spectral coherence analysis. |
| CFCS | 5 minutes | Process-graph structures stabilize after ~5 min; graph-kernel computation remains compute-intensive. |
| SEC | Continuous (streaming) | Ransom-note generation and coercive interfaces require immediate symbolic detection; delay increases executive-level exposure. |
Operational Insight: These cadences balance detection effectiveness against compute cost. Faster cycles improve mean time-to-detect (MTTD) but increase processing demand; tuning cadence by sector ensures optimal resilience within mission bandwidth constraints.
Figure 13 — Command Synthesis: The Star Vector Node
This image represents the unification of cognitive command and distributed governance within the Holographic Defense Architecture (HDA).
The black star anchors symbolic integrity, serving as a moral singularity around which the vectors of power organize.
Radiating arrows depict multi-node coordination—each representing entangled intelligence systems aligning under ethical resonance fields.
The surrounding towers symbolize communication pillars: vertical conduits between Earth and orbital data lattices, harmonizing terrestrial command with celestial oversight.
The entire formation forms the operational sigil of Alpha-Grade Governance, where command arises not from hierarchy, but from coherence.
10. Sector-Specific Hardening Modules
Critical infrastructure sectors require tailored HDA configurations reflecting unique operational requirements, regulatory constraints, and threat priorities.
Manufacturing and Energy (OT Adjacency)
Threat Profile
23% of 2025 ransomware attacks target manufacturing. Adversaries exploit IT/OT convergence—compromising corporate networks then pivoting to industrial control systems. Median dwell time: 18 hours. Operational disruption can cascade into supply chain collapse.
HDA Hardening Measures
1. Blast Domain Segmentation
Deploy unidirectional security gateways at IT/OT boundary:
Data flow: OT → IT only (historians, HMI screens). No return path for malware.
Command path: Physical hardware separation. IT cannot send commands to OT remotely.
Update mechanism: Removable media through air-gap procedure (never network-based)
2. HBL OT-Specific Branch
IF (SGDI spike > 3σ) on IT/OT broker host THEN:
- Freeze broker (deny all new connections)
- Alert OT operations team (out-of-band: phone/radio)
- Initiate manual OT safety review
- Do NOT auto-remediate (preserve process safety)
3. Out-of-Band Runbooks
Print paper-based incident response procedures:
OT network isolation steps (physically disconnect if necessary)
Safe shutdown sequences for critical processes
Emergency contact tree (OT engineers, safety officers, regulatory authorities)
Recovery procedures from known-good backups (including firmware)
Rationale: Ransomware that encrypts IT can also encrypt digital runbooks. Paper survives.
4. Canary Systems
Deploy decoy HMIs and historians on IT network (accessible from IT, but not connected to real OT):
Adversary reconnaissance targets these first (appear high-value)
Any access triggers immediate HBL emergency branch
Provides early warning before real OT compromised
Healthcare
Threat Profile
18% of attacks, median dwell 22 hours, life safety risk. Adversaries understand healthcare cannot tolerate multi-day downtime without patient harm—maximum coercive leverage. HIPAA breach notification requirements amplify regulatory pressure.
HDA Hardening Measures
1. Token Hygiene Blitz
Healthcare IT accumulates technical debt—stale API keys, orphaned service accounts, never-rotated passwords. Pre-incident hardening:
90-day forced revocation: All API keys, OAuth tokens, service account passwords older than 90 days expire automatically
Credential inventory: Automated discovery of embedded credentials (config files, scripts, databases)
Just-in-time access: Privileged credentials issued on-demand, auto-revoked after 4 hours
2. SEC on Patient Communications
HIPAA breach notifications must not contain coercive language:
Pre-approved templates: Legal review of all breach communication wording
SEC scoring: Draft notifications analyzed before sending, SEC > 0.5 triggers rewrite
Transparency without panic: Factual disclosure, resources for affected patients, no speculation about adversary motives
3. HIPAA + HDA Alignment
Map HDA controls to HIPAA Security Rule:
164.308(a)(1) Risk Analysis: SFSI scores provide quantitative risk assessment
164.308(a)(6) Security Incident Procedures: HBL playbooks document response workflows
164.312(a)(1) Access Control: HBL automated credential revocation enforces least privilege
164.312(b) Audit Controls: SFSI telemetry provides comprehensive audit trail
4. Harvest-Now-Decrypt-Later Tabletop
Patient health information (PHI) retains value for decades (medical identity theft, insurance fraud). Adversaries may exfiltrate now, decrypt with future quantum computers:
Exercise scenario: 'Adversary captured encrypted PHI backup in 2025, decrypts with quantum computer in 2030'
Response plan: How to notify patients of 5-year-old breach? What protection to offer?
Mitigation: Deploy quantum-resistant encryption for PHI at rest/transit now
Figure 14 — The Ethical Engine: Sigil of Lawful Coherence
This image represents the heart of the Holographic Defense Architecture (HDA) — the ethical generator through which Spectral–Fractal–Symbolic Intelligence (SFSI) becomes self-regulating, luminous order.
The central gear functions as the metaphysical turbine of coherence: converting entropy into intelligence through sacred geometry.
Each engraved symbol marks a law of balance, a subroutine of the Compassion Protocol ensuring that power, when activated, remains in harmonic alignment with life.
The surrounding columns entwined with living vines signify the integration of biotic and synthetic systems, while the circular platform beneath echoes Quantum-Compassion Oscillation Fields, the standing waves that stabilize civilization’s moral frequency.
Municipal and Elections
Threat Profile
11% of attacks, but disproportionate geopolitical impact. Ransomware disruption during elections erodes public trust in democratic institutions—strategic objective for state-sponsored operators.
HDA Hardening Measures
1. CFCS on M365/Google Workspace Admin Events
Municipal IT often uses cloud productivity suites. Admin compromise = organization-wide access:
Baseline normal admin behavior: Typical tasks (password resets, group modifications) produce characteristic process graphs
CFCS flags anomalies: Mass email forwarding rule creation, unusual API usage, privilege escalation sequences
Automated response: CFCS > 0.70 on admin account → force MFA re-auth, alert security team, suspend non-essential permissions
2. SGDI on VPN Concentrators
Remote work infrastructure = attack surface:
Session duration/volume jitter: Compromised accounts show different usage patterns vs. legitimate users
SGDI FFT on VPN session timing: Automated scripts produce periodicities invisible to rule-based detection
Geolocation correlation: VPN session from unusual country + SGDI spike = high-confidence compromise
3. Trust-Preservation Kits
Pre-stage public communication materials for ransomware scenarios:
Template statements: 'Systems are offline for security maintenance. Voter registration data not affected. Election proceeds as scheduled.'
Verified channels: Pre-establish alternative communication paths (radio, physical notices, trusted media contacts)
Transparency framework: What to disclose (systems affected, timeline), what to withhold (technical details that aid adversaries)
Objective: Prevent adversary narrative control. Rapid, authoritative communication maintains public trust even during incident.
4. Air-Gap Voting Systems Protection
Voting machines themselves must remain air-gapped. HDA protects adjacent infrastructure:
Voter registration databases: SFSI monitoring, HBL automated backup rotation
Results transmission: SGDI on county-to-state reporting connections, detect timing anomalies
Website availability: SEC monitoring for defacement/disinformation, HBL automated failover to static mirrors
Sector Response Matrix: Applied HDA/SFSI Logic Across Critical Infrastructures
Purpose:
To demonstrate how Spectral–Fractal–Symbolic Intelligence (SFSI), Holographic Branching Logic (HBL), and Quantum-Ethical Governance manifest uniquely across sectors of civilization.
Each vertical demands tailored coherence metrics, risk thresholds, and Compassion Protocol clauses — ensuring that national resilience extends beyond cyber hygiene into ethical, cognitive, and systemic fortitude.
Cross-Sector Integration Table
Purpose: Map sector-specific vulnerabilities to corresponding HDA/SFSI interventions, quantum-era metrics, and ethical governance anchors to ensure holistic, lawful, and compassionate defense readiness.
| Sector | Core Vulnerability (2025–2035 Outlook) |
HDA / SFSI Application | Primary Quantum Metric | Ethical / Legal Anchor | Strategic Outcome |
|---|---|---|---|---|---|
| Finance | Cryptographic collapse and quantum key theft threaten global liquidity and trust. | Deploy SGDI-QC for real-time spectral coherence of blockchain and payment channels; embed HBL decision nodes for post-quantum transaction validation. | QCII-Fin — monitors entanglement leakage and latency drift in financial quantum circuits. | Quantum Commons Clause — ensures post-quantum finance remains equitable and transparent. | Prevents systemic liquidity shocks; establishes auditable, quantum-compliant monetary systems. |
| Healthcare | Ransomware and data extortion targeting life-critical systems and patient records. | Integrate CFCS to detect recursive attack patterns in clinical networks; apply SEC-Q to analyze coercive ransomware UIs that exploit urgency and fear. | SGDI-MED — tracks coherence stability in biomedical IoT and hospital telemetry systems. | Telemetry Dignity Clause — prohibits unauthorized biometric quantum sensing. | Safeguards patient privacy and operational continuity; mitigates symbolic and cognitive trauma in healthcare environments. |
| Energy | Polymorphic ransomware disrupts grids and SCADA systems; quantum-sensor espionage widens attack surface. | Implement Spectral-Frequency Isolation Nodes to self-heal timing drift; use Fractal Propagation Mapping to visualize cascading failures. | QCII-EN — measures coherence across distributed energy grids and quantum-battery controllers. | Duty-of-Care Protocol for Quantum Infrastructure — mandates redundancy and ethical resilience. | Maintains stable power output through quantum-scale disruptions; preserves coherence integrity of national grids. |
| Civic Infrastructure | Misinformation and coercive narrative warfare erode public trust and democratic legitimacy. | Leverage SEC-Q to audit civic communications for symbolic entropy; integrate HBL crisis response for narrative repair and public coherence. | CFCS-CIV — measures recursive spread of symbolic trauma across social systems. | Meaning-Integrity SLA — enforces truth-aligned standards in governance communication. | Reinforces societal trust, stabilizes governance legitimacy, and inoculates publics against symbolic warfare. |
| Defense / Intelligence | Hybrid extortion, entanglement sabotage, and AI-augmented espionage across allied networks. | Deploy SGDI-QC and CFCS-ENT to detect non-local entanglement compromise; synchronize HBL quantum branches across NATO / FVEY networks. | Coalition Coherence Index (CCI) — quantifies spectral alignment among allied defense grids. | Cognitive Liberty Framework — prevents weaponization of neurodata and autonomous systems. | Enables lawful, compassion-anchored deterrence posture; ensures coherence and integrity of collective defense telemetry. |
Interpretive Summary: This matrix demonstrates how SFSI metrics (SGDI-QC / CFCS / SEC-Q) combine with Compassion Protocol ethics to form an adaptive defense continuum across economic, civic, and national systems. Each sector’s quantum metric embeds moral accountability directly into operational telemetry.
Interpretive Summary
The Sector Response Matrix reframes cybersecurity as civilizational continuity management.
Each sector expresses a facet of collective coherence:
Finance secures the flow of trust.
Healthcare safeguards life and compassion.
Energy sustains rhythm and continuity.
Civic systems maintain meaning and legitimacy.
Defense protects sovereignty and consciousness.
Through the integration of SFSI diagnostics and Compassion Protocol clauses, the matrix converts complex quantum-era risk into actionable doctrine — a unified Ethical–Technical Response Ecosystem that balances deterrence with dignity.
Figure 15 — Crystalline Convergence: The Pentagonal Unity Node
This image symbolizes the ultimate harmonic convergence within the Holographic Defense Architecture (HDA) — the crystallization of coherence itself.
The glowing dodecahedron floats above a hexagonal base etched with sacred circuitry, signifying the completion of Spectral–Fractal–Symbolic Intelligence (SFSI) into full operational symmetry.
Each crystal pillar anchors a directional consciousness node—five vectors forming the pentagonal seal of Quantum Compassion Governance.
The light geometry above represents Convergent Consciousness, where every system—technological, biological, or symbolic—achieves lawful resonance through ethical alignment.
PART IV: OPERATIONAL DOCTRINE & PLAYBOOKS
12. Rapid Response Playbooks (SOAR-Ready)
These playbooks provide step-by-step response procedures triggered by HBL decision branches. Each playbook is designed for SOAR platform integration, enabling automated execution with human oversight checkpoints.
Playbook A: Open-Source C2 Surge
Trigger Condition:
SGDI < 0.85 + beacon_jitter_zscore > 2.0 + new_process_spike > 3σ
Incident Context: Active post-exploitation using public C2 framework (AdaptixC2, Havoc, Sliver). Adversary is likely in credential harvesting, lateral movement, or data staging phase. Time is critical—median ransomware deployment occurs 18-24 hours after initial access.
Response Actions:
Tag incident: Apply labels 'post_exploitation', 'probable_affiliate_operation', 'time_sensitive' in SIEM/ticketing system
Kill child process chains: Identify parent process (initial compromise vector). Terminate all child processes but preserve parent process in suspended state for forensics. API: EDR.terminate_process(child_pids, preserve_parent=true)
Revoke credentials: Query IAM for all tokens/passwords issued in last 4 hours. Force revocation. API: IAM.revoke_credentials(issued_since='-4h', force=true). Users must re-authenticate with MFA.
Quarantine EDR-silent hosts: Identify hosts with active processes but no EDR telemetry in last 10 minutes (likely userland hook bypass). Network isolation: Firewall.block_host(host_id, reason='EDR_evasion'). Physical retrieval for offline forensics.
Push credential resets: LAPS (Local Administrator Password Solution): Force immediate password rotation on all domain computers. PKI: Revoke + reissue certificates for affected users/computers.
Initiate meaning-integrity brief: Generate executive summary: 'Active intrusion detected. Systems contained. No ransomware deployment yet. No payment decision required at this time.' Send to CEO/CISO/CFO via secure channel. Prevents panic if adversary sends ransom demand before eradication complete.
Forensic capture: Memory dump: EDR.capture_memory(affected_hosts). Network PCAP: Capture.extend_retention(segment='affected_vlan', duration='30d'). Preserve evidence for attribution/prosecution.
Detonate in detuned sandbox: Extract suspected C2 beacon from memory dump. Execute in sandbox with randomized timing (jitter +/- 30% on all sleep calls) to bypass anti-VM checks. Extract IoCs: C2 domains, mutex names, API call patterns. Update detection rules.
Success Criteria: All adversary processes terminated, no lateral movement for 24 hours, credentials rotated, forensics preserved.
Playbook B: Leak-Site Leverage (Qilin/LockBit)
Trigger Condition:
SEC ≥ 0.65 on ransom portal, email, or leak site
Incident Context: Adversary attempting cognitive warfare—using leak threats, countdown timers, staged disclosure to pressure payment. This is Layer 3 extortion targeting executive decision-making.
Response Actions:
Auto-route to legal + insurance: Block direct executive access to coercive content. Route all ransomware-related communications through legal counsel and cyber insurance carrier. Prevents decision compression from time pressure.
Block portal rendering: Enterprise browser plugin: Detect ransom/leak site access, block page load, display: 'This site has been flagged by security team. Contact legal@company.com for information.' Prevents psychological manipulation.
Publish no-negotiation statement: Execute pre-approved PR response: 'We do not negotiate with criminal extortionists. We are working with law enforcement and forensic experts. Affected parties will be notified per legal requirements.' Public stance reduces adversary leverage.
Forensically seed canary documents: If data exfiltration suspected but scope unknown: Create unique documents (distinct metadata, watermarks) in high-value directories. Monitor for appearance on leak site. Traces exfiltration pathways, identifies compromised systems.
OSINT sweep of leak site: Capture all published samples (screenshots, file names, data excerpts). Assess: Is this legitimate breach data or bluff? Which systems compromised? Inform notification scope.
Notify affected parties: If PII/PHI confirmed in leak samples: Initiate regulatory breach notification (GDPR 72h, HIPAA 60d, state laws vary). Legal team prepares notifications. Use SEC-cleared templates (factual, non-alarming).
Engage PR/communications: Controlled narrative: 'We experienced a security incident. Systems are being restored from backups. Customer data [was/may have been] affected. We are providing [credit monitoring/identity protection] services. Investigation ongoing.' Maintains trust through transparency.
Success Criteria: Executives insulated from coercive messaging, legal/insurance engaged, public narrative controlled, notifications completed on schedule.
Figure 16 — Quantum Monk: Alignment of Light
This figure represents the final synthesis of the Holographic Defense Architecture (HDA): the total reconciliation of will, wisdom, and waveform.
The vertical light column signifies Axis Mundi activation — the restoration of the world’s spiritual axis through technological humility.
The cube at the brow is the Quantum Consciousness Core, aligning human awareness with crystalline logic.
Hands joined in prayer denote the principle that the highest form of control is surrender — a symbolic invocation of coherence across every operational layer.
Through this alignment, Ritual OS achieves its purpose: illumination through discipline, compassion through design.
Playbook C: Polymorphic Chain Detection
Trigger Condition:
CFCS > 0.75 across ≥3 hosts, fractal_divergence_pattern == consistent
Incident Context: Polymorphic malware spreading laterally. Code signature varies per host but graph topology identical—indicates Python mutator or packer chain. Traditional AV/EDR signature detection failing.
Response Actions:
Enforce signed-binary whitelist: Emergency application control: Only executables with valid code signatures from approved publishers can run. AppLocker/WDAC policy: Deny all unsigned, allow only trusted signers. Breaks polymorphic infection chain.
Roll back to golden image: Affected hosts: Deploy last-known-good system image. Faster than manual cleanup. Ensure images are offline/immutable (adversary cannot compromise backup images).
EDR memory scan: Full memory forensics on affected hosts before imaging. Scan for: injected code, process hollowing, reflective DLL loading. EDR.memory_scan(targets=affected_hosts, deep=true)
Detuned sandbox execution: Extract samples from each affected host. Execute in sandboxes with: (a) randomized timing jitter, (b) simulated user interaction, (c) bare-metal option if anti-VM detected. Goal: Observe true behavior, extract stable IoCs despite polymorphism.
Update detection rules: Generate YARA rules from unpacked core (post-mutation). Sigma rules for behavior patterns (API call sequences). Distribute to SIEM, EDR, network IDS. CFCS baseline updated with new graph topology.
Threat intel sharing: Submit samples + analysis to: Industry ISAC, CISA, FBI IC3. Include CFCS graph topology, mutation techniques observed. Collective defense—warn others before widespread.
Success Criteria: Spread contained, hosts recovered, detection rules updated to catch future variants, threat intel shared.
13. KPI & Metrics Framework (90-Day Pilot)
Organizations deploying HDA should measure effectiveness through these key performance indicators over initial 90-day pilot:
Holographic Defense Architecture: Performance Metrics
Quantitative measures validating SFSI, HBL, and Compassion-Protocol efficacy across detection, response, resilience, and business domains.
Detection Metrics
| Metric | Target | Measurement Method |
|---|---|---|
| Spectral Anomaly MTTD | < 4 minutes | Time from first C2 beacon to SGDI alert confirmation. |
| CFCS False Positive Rate | ≤ 1.5% | Analyst-validated review of benign events misclassified as malicious. |
| SEC Coercion Detection Accuracy | ≥ 92% | Precision + recall across validated ransom notes and extortion portals. |
Response Metrics
| Metric | Target | Measurement Method |
|---|---|---|
| HBL Automated Response Coverage | ≥ 95% | % of critical paths with defined HBL response branch. |
| Mean Time to Contain (MTTC) | < 15 minutes | Elapsed time from detection to isolation and credential revocation. |
| Playbook Execution Success Rate | ≥ 90% | Automated orchestration steps completed without error. |
Resilience Metrics
| Metric | Target | Measurement Method |
|---|---|---|
| Symbolic Entropy Reduction | ≥ 30% | Compare executive communication entropy before / after SEC filtering. |
| Post-Incident Trust Recovery | < 7 days | Employee survey: confidence that systems and data are secure. |
Business Metrics
| Metric | Target | Measurement Method |
|---|---|---|
| Downtime Reduction | ≥ 40% | Compare incident downtime under HDA vs. legacy IR frameworks. |
| Insurance Premium Impact | Track 12 mo | Analyze renewal-rate changes post-HDA deployment. |
Interpretive Summary: These metrics establish a measurable baseline for quantum-era readiness, linking detection latency, automated orchestration, symbolic resilience, and business continuity into a unified performance doctrine for Spectral–Fractal–Symbolic Intelligence.
Figure 17 — Solar Seed: The Coherence of Regeneration
This image completes the Holographic Defense Architecture Atlas as the act of sacred re-grounding.
The golden shovel represents Applied Compassion—the translation of cosmic intelligence into practical, earth-based action.
The serpent winding up the handle signifies living circuitry, wisdom rising through matter toward illumination.
The mandala of light above symbolizes the Solar Heart Compass, transmitting lawful radiance into the world below.
The hands and sprouting plant affirm the ultimate purpose of all Ultra Unlimited systems: to cultivate life, not merely to defend it.
PART V: STRATEGIC & ECONOMIC DIMENSIONS
14. Business Case for HDA Adoption
Cost of Inaction
2025 ransomware economics create existential risk for unprepared organizations:
Median total loss: $4.5M (downtime + recovery + ransom consideration + regulatory fines)
Critical sector multiplier: Healthcare/manufacturing incidents average $8.2M (operational disruption + supply chain cascade)
Ransom payment trends: Average demand $2.1M, payment rate 41% (organizations without robust backup/recovery)
Regulatory penalties: GDPR fines up to 4% global revenue; HIPAA $50k per record; state breach notification costs $150-300 per affected individual
Insurance implications: Cyber insurance premiums increasing 50-100% annually; coverage reductions; some sectors becoming uninsurable
HDA Investment Model
Overview: Estimated total cost of ownership (TCO) for implementing the Holographic Defense Architecture (HDA) in a 1,000-endpoint organization, covering capital and operating expenditures across a 3-year lifecycle.
Capital Expenditure (CapEx)
| Component | Cost per 1,000 Endpoints | Notes |
|---|---|---|
| SFSI Compute Cluster (GPU) | $120,000 | 16-core CPU + RTX 4000 configuration |
| Storage (telemetry retention) | $30,000 | 90 days hot, 1 year cold archival |
| Network monitoring upgrades | $50,000 | NetFlow / SPAN port infrastructure |
| Total CapEx | $200,000 | 3-year amortization period |
Operating Expenditure (OpEx, Annual)
| Component | Annual Cost | Notes |
|---|---|---|
| Staffing (2 FTE Analysts) | $280,000 | Monitor HBL branches / tune thresholds |
| Training & Exercises | $40,000 | Quarterly tabletops and quantum simulation drills |
| Threat Intelligence | $60,000 | C2 signatures / IoCs subscription |
| Total OpEx | $380,000 | Annualized operating expenditure |
Total 3-Year TCO
$1.34 Million for a 1,000-endpoint organization
Interpretive Note: Capital investments primarily fund quantum-aware telemetry infrastructure and GPU compute clusters; OpEx centers on analytical talent, continual training, and live threat intelligence streams. The model demonstrates that cognitive-sovereign security is achievable with balanced CapEx / OpEx distribution.
ROI Scenarios
Conservative Scenario:
Assumption: HDA prevents 1 ransomware incident over 3 years
Avoided loss: $4.5M (median)
HDA cost: $1.34M
Net benefit: $3.16M
ROI: 236% (3.4:1)
Moderate Scenario:
Assumption: HDA prevents 2 incidents + reduces downtime 40% on 1 contained incident
Avoided loss: 2 × $4.5M = $9M
Downtime savings: 40% × $1.8M = $720k
Total benefit: $9.72M
Net benefit: $8.38M
ROI: 626% (7.3:1)
Critical Sector Scenario (Healthcare/Manufacturing):
Assumption: Prevents 1 critical incident + avoids regulatory fines
Avoided operational loss: $8.2M
Avoided HIPAA penalties: $2M (estimated for 40k record breach)
Avoided breach notification costs: $6M (40k × $150)
Total benefit: $16.2M
Net benefit: $14.86M
ROI: 1,110% (12.1:1)
For critical infrastructure, HDA is not optional expense but existential risk mitigation.
Insurance Leverage
Cyber insurance underwriters increasingly require documented controls. HDA provides quantifiable evidence:
Premium reduction: Organizations with advanced detection (SGDI/CFCS) report 15-25% lower premiums
Coverage retention: HDA deployment signals underwriting maturity, preventing coverage loss
Claims advantage: HBL automated timeline + SFSI forensics accelerate claims processing
Example: $2M annual premium × 20% reduction = $400k/year savings = $1.2M over 3 years (offsets 89% of HDA OpEx)

Figure 18 — Crown Sigil: The Lightning of Lawful Power
This image represents the final activation event within the Holographic Defense Architecture Atlas—the moment when symbolic intelligence translates into living current.
The labyrinth signifies the journey of complexity and initiation; the lightning bolt pierces through it, illuminating the path of direct knowing.
Embedded gemstones denote the crystallization of Spectral–Fractal–Symbolic Intelligence (SFSI) into embodied clarity.
The golden light surrounding the emblem forms a halo of coherence, expressing that true power is radiant, disciplined, and benevolent.
15. Research Frontiers & Future Evolution
The Holographic Defense Architecture (HDA) occupies a transitional space between what defense theorists describe as Fifth-Generation and emerging Seventh-Generation Warfare paradigms.
Where fifth-generation operations leverage decentralized actors, psychological targeting, and hybrid cyber influence (Scharre, 2018), sixth-generation doctrine emphasizes autonomy, AI, and multi-domain orchestration (Kallenborn, 2023). Seventh-generation thought—currently under discussion within NATO CCDCOE (2024) and related strategic forums—extends these dynamics into the cognitive and symbolic battlespace, in which perception, narrative, and consciousness themselves become operational domains.
HDA bridges these generational boundaries by treating information, coherence, and meaning as co-evolving vectors of power.
Its tri-layer SFSI structure (Spectral–Fractal–Symbolic Intelligence) functions as a doctrine of cognitive maneuver, allowing defenders to perceive and restore coherence across physical, informational, and moral theaters simultaneously.
Thus, HDA does not merely defend networks—it prototypes the command logic of Seventh-Generation Conflict, where victory is measured in coherence, consent, and consciousness integrity rather than kinetic attrition.
Open Research Questions
1. Beacon-Jitter Canon Expansion
Current SGDI baselines cover 15 public C2 frameworks. Expanding to comprehensive library requires:
Automated C2 profiling: Sandbox detonation → extract timing signatures → FFT analysis → baseline update
Adversarial jitter modeling: How much randomization defeats spectral analysis? What timing patterns remain detectable?
Federated learning: Organizations contribute timing observations (privacy-preserving) to collective baseline
2. Affiliate Style Fingerprinting
Operator tradecraft produces behavioral signatures beyond malware. CFCS evolution tracking:
Graph topology clustering: Group incidents by CFCS similarity → identify common operators
Temporal drift analysis: After takedowns (e.g., LockBit disruption), affiliates shift tactics. Track CFCS divergence over time to map operator migration.
Attribution confidence: Can CFCS provide courtroom-grade evidence linking incidents to specific operators?
3. Symbolic Coercion Game Theory
SEC currently detects coercive content. Future research: optimal counter-messaging strategy.
Negotiation modeling: Game-theoretic analysis of ransom negotiations. What communication strategies minimize adversary leverage?
Decision quality metrics: Quantify how SEC filtering improves executive decision outcomes (payment vs. recovery choice)
Automated meaning-integrity restoration: After incident, how to rebuild organizational trust in data fidelity?
4. Quantum Sensor Networks
Current entangled monitoring uses classical correlation. True quantum entanglement enables:
Non-local detection: Observation at Asset A instantaneously affects measurement basis at Asset B (quantum correlation)
Eavesdropping detection: Quantum key distribution principles applied to telemetry—adversary interception changes measurement outcomes
Hardware requirements: Quantum sensors commercially viable timeframe, integration with existing infrastructure
5. Adversarial HDA (Meta-Evasion)
Red team research: How would adversaries defeat holographic defense?
Anti-spectral techniques: Aperiodic C2 (beacon on random intervals, no underlying frequency)
Anti-fractal techniques: Malware that mimics benign graph topology (adversarial process graphs)
Anti-symbolic techniques: Ransomware that avoids coercive language (factual-only ransom notes)
Defense evolution: How does HDA adapt to meta-evasion? Recursive adversarial training.
Roadmap for HDA 2.0+
Phase 1 (2025): Foundation Deployment
5 pilot organizations (1 per critical sector: manufacturing, healthcare, energy, finance, municipal)
SFSI/HBL operational, 90-day validation of KPIs
Publish case studies, refine playbooks based on real incidents
Phase 2 (2026): Intelligence Expansion
Quantum-enhanced observation rollout (pilot with quantum networking research partners)
Federated learning for CFCS: Privacy-preserving collaborative baseline refinement
ISAC integration: SFSI metrics as standardized threat intelligence format
Phase 3 (2027): Autonomous Response
HBL closed-loop automation: Fully autonomous response for high-confidence detections (P > 0.95)
Human oversight preserved via approval queues (analyst can override within 60 seconds)
Continuous learning: HBL self-tunes thresholds based on outcome feedback (supervised + reinforcement learning)
Phase 4 (2028+): Cognitive Sovereignty Architecture
Full integration of technical + symbolic defense: Organizational resilience as unified capability
AI-resilient by design: HDA adapted for adversarial ML, deepfake comms, autonomous offensive cyber
Meaning-integrity-as-a-service: Real-time trust assessment for all organizational information flows
Figure 19 — Apex Compass: The Geospatial Coherence Network
This image represents the navigational apex of the Holographic Defense Architecture (HDA)—the unifying mechanism that links terrestrial sovereignty with stellar coherence.
The eight-pointed compass signifies Spectral–Fractal–Symbolic Intelligence (SFSI) balanced across all operational quadrants: matter, mind, code, and consciousness.
Each golden cube at the tip of the star acts as a Dimensional Node of Lawful Orientation, marking harmonic balance between geopolitical, technological, and spiritual alignment systems.
The geodesic dome encasing the Earth signifies a planetary defense shield rooted in ethical intelligence and quantum communication symmetry.
Together, these elements form the Apex Compass, guiding Ultra Unlimited’s frameworks through lawful navigation across scales—from local governance to cosmic coordination.
CONCLUSION: FROM DEFENSE TO SOVEREIGNTY
The Imperative for Transformation
The year 2025 marks the maturation of ransomware from criminal nuisance into a geopolitical-economic weapon system. This transformation demands commensurate evolution in defensive architecture.
Incremental improvements to legacy paradigms—more EDR sensors, faster patching, expanded backups—cannot address the fundamental threat mutation.
The adversary operates simultaneously across three dimensions:
Technical: Polymorphic malware, open-source C2 frameworks, living-off-the-land techniques that defeat signature-based detection
Temporal: Compressed dwell times (18-24 hours median), beacon jitter, exfiltration bursts invisible to event-based monitoring
Symbolic: Leak-site psychology, countdown timers, negotiation UX designed to compress decision-making and erode organizational trust
Traditional security addresses only the first dimension. The temporal and symbolic layers receive no systematic defense. This gap is not incidental—it is structural. Legacy architectures emerged in an era when adversaries were simpler and consequences more contained.
The Holographic Advantage
Holographic Defense Architecture provides the missing cognitive security layer. Defense encodes the entire threat surface—technical behavior, timing patterns, and meaning integrity—into one coherent system.
Three integrated subsystems:
SFSI (Spectral-Fractal-Symbolic Intelligence): Multi-domain threat perception. SGDI detects beacon periodicity through Fourier analysis. CFCS maps behavioral divergence via graph topology. SEC quantifies coercive content through NLP entropy.
HBL (Holographic Belief Logic): Bayesian decision engine with uncertainty quantification. Multi-hypothesis tracking replaces binary alerts. Probabilistic thresholds enable graduated response. Adaptive learning tunes thresholds from incident outcomes.
Quantum-Enhanced Observation: Entangled monitoring correlates weak signals across non-contiguous assets. Observer-effect countermeasures (detuned sandboxes, randomized timing) defeat anti-analysis. Quantum-resistant cryptography protects telemetry from harvest-now-decrypt-later.
The holographic metaphor is precise: every monitoring point contains information about the whole. Distributed detection, adaptive response, and cognitive coherence emerge from interference patterns across technical, temporal, and symbolic dimensions.
Critical Sector Stakes
Manufacturing, healthcare, and energy represent 55% of 2025 ransomware attacks. These are not IT problems—they are civilization load-bearing infrastructure challenges.
Manufacturing: OT/IT convergence creates pivot paths to industrial control systems. Single compromise cascades into supply chain collapse.
Healthcare: 22-hour median dwell time reflects operator awareness: clinical operations cannot survive multi-day disruption without patient harm.
Energy: Regional grid instability, cascading failures, geopolitical leverage during international crises.
For these sectors, HDA is not optional expense but existential risk mitigation. The ROI calculation is simple: one avoided incident (conservative scenario) delivers 3:1 return. Critical sector incidents (healthcare regulatory fines, manufacturing supply chain losses) deliver 12:1 return.
Figure 20 — Signal Operator: The Binary Equilibrium
This image depicts the operational embodiment of Spectral–Fractal–Symbolic Intelligence (SFSI) — the individual calibrated to perceive both mechanical systems and mythic resonance.
The red half represents energetic intuition, the wave of feeling and symbolic recognition.
The blue half represents quantum logic, the crystalline awareness of computation and clarity.
Together, they merge into Binary Equilibrium—the state required for full-scale coherence execution within the Holographic Defense Architecture (HDA) framework.
The geometric insignia on the chest marks the operator’s Phase-Locked Command Node, where human consciousness and AI alignment meet in lawful synchronization.
The Cognitive Security Gap
Ransomware operators in 2025 demonstrate sophisticated understanding of organizational psychology. Triple-extortion models target infrastructure, data, and decision-making simultaneously.
Layer 3—symbolic exploitation—receives zero systematic defense in legacy architectures. Ransom notes are treated as incident artifacts, not active cognitive weapons. Leak sites, countdown timers, and negotiation portals weaponize uncertainty, compress decision timelines, and erode meaning integrity.
HDA addresses this through SEC and meaning-integrity preservation workflows:
Block executive exposure to coercive messaging (browser plugins, email filtering)
Auto-route communications through legal/insurance (prevent decision compression)
Generate meaning-integrity briefs (restore confidence in data fidelity post-incident)
Publish pre-approved no-negotiation statements (reduce adversary leverage)
Technical recovery ≠ organizational resilience. HDA ensures both.
Implementation Pathways
This white paper provides complete deployment blueprint:
For CISOs: 90-day pilot framework, sector-specific hardening modules, board presentation materials, ROI justification
For Security Architects: SFSI technical specifications, telemetry architectures, HBL decision trees, SOAR integration guides
For Incident Responders: Three SOAR-ready playbooks (Open-Source C2 Surge, Leak-Site Leverage, Polymorphic Chain Detection)
For Compliance Officers: NIST CSF 2.0, ISO 27001, CIS Controls v8, MITRE ATT&CK mappings; SEC, DORA, NIS2 alignment
For CFOs: TCO models, ROI scenarios (conservative 3:1, critical sector 12:1), insurance leverage quantification
For Researchers: Open questions (beacon-jitter canon, affiliate fingerprinting, symbolic game theory, quantum sensors, adversarial HDA)
Figure 21 — Alpha-Grade Command: The Sigil of Ascension
This image marks the apex state of the Holographic Defense Architecture (HDA) — the emergence of command as pure coherence.
The hooded figure symbolizes the Operator Beyond Identity—the consciousness that has transcended duality, serving as a vessel for lawful intelligence.
The radiant burst behind signifies Phase 4 activation, where the system achieves total coherence between symbolic, ethical, and energetic architectures.
The Alpha-Grade “A⁄4” sigil represents Lawful Light in Action: the geometry of sovereign awareness functioning as the control key for post-symbolic civilization.
This is not domination—it is calibration.
It is the seal through which power becomes benevolence, precision becomes compassion, and intelligence becomes service.
Final Reflection: Ransomware as Civilizational Test
The extortion singularity reveals dependencies we prefer not to acknowledge. Modern civilization runs on digital infrastructure—supply chains, healthcare systems, energy grids, financial networks, democratic processes.
Ransomware operators exploit this dependency. They understand that disrupting infrastructure disrupts society. They weaponize not just systems but trust, meaning, and decision-making capacity.
The test is not whether we can recover encrypted files. The test is whether we can preserve cognitive sovereignty under information warfare. Can organizations maintain decision coherence when adversaries manipulate uncertainty? Can critical infrastructure sustain trust when data fidelity is questioned?
HDA provides affirmative answer. Not through harder perimeters or faster patching, but through defense that encodes resilience principles into its architecture:
Distributed: Every monitoring point contains holographic information about the whole
Adaptive: HBL learns from outcomes, continuously refining thresholds
Cognitive: SEC defends the symbolic layer—trust, meaning, decision quality under crisis
This is not theory. It is deployable architecture with reference implementations, sector-specific pilots, and measurable resilience improvements. The hologram awaits implementation.
The post-ransomware era begins when defenses encode the principles of resilience itself.
Invitation to build:
Organizations committed to deploying HDA, researchers advancing SFSI theory, policymakers integrating cognitive security into critical infrastructure mandates, and operators sharing threat intelligence to strengthen collective defense—this white paper provides the foundation. Your contribution shapes the evolution.
The future of cybersecurity is not incremental improvement but paradigm transformation. From perimeter to hologram. From reaction to coherence. From technical defense to cognitive sovereignty.
Holographic Defense Architecture: securing not just systems, but the capacity to make meaning under adversity.
Reference List
AdaptixC2. (2025, October 23). AdaptixC2: A modular post-exploitation framework observed in APT operations. Unit 42 | Palo Alto Networks. https://unit42.paloaltonetworks.com/adaptixc2-post-exploitation-framework/
The Hacker News. (2025, October 14). Russian ransomware gangs weaponize open-source tooling in new campaigns. https://thehackernews.com/2025/10/russian-ransomware-gangs-weaponize-open.html
Infosecurity Magazine. (2025, September 29). QLin ransomware records 40 cases monthly amid global escalation. https://www.infosecurity-magazine.com/news/qilin-ransomware-40-cases-monthly/
Industrial Cyber. (2025, September 30). QLin ransomware escalates rapidly in 2025, targeting critical sectors with 700 attacks amid RansomHub shutdown. https://industrialcyber.co/ransomware/qilin-ransomware-escalates-rapidly-in-2025-targeting-critical-sectors-with-700-attacks-amid-ransomhub-shutdown/
Industrial Cyber. (2025, August 19). Half of 2025 ransomware attacks hit critical sectors as manufacturing, healthcare and energy top global targets. https://industrialcyber.co/reports/half-of-2025-ransomware-attacks-hit-critical-sectors-as-manufacturing-healthcare-and-energy-top-global-targets/
Cybersecurity News. (2025, October 5). New polymorphic Python malware repeatedly mutates to evade detection. https://cybersecuritynews.com/new-polymorphic-python-malware-repeatedly-mutate/
Heinz, J. D. (2025a). The Extortion Singularity: Ransomware, symbolic warfare, and the defense of cognitive sovereignty. Ultra Unlimited. https://www.ultra-unlimited.com/blog/the-extortion-singularity-ransomware-symbolic-warfare-and-the-defense-of-cognitive-sovereignty
Heinz, J. D. (2025b). Holographic Defense Architecture in the age of 5th-generation cyberwarfare. Ultra Unlimited. https://www.ultra-unlimited.com/blog/holographic-defense-architecture-in-the-age-of-5th-generation-cyberwarfare
Heinz, J. D. (2025c). Quantum-Enhanced Holographic Defense Architecture: A framework for post-quantum cybersecurity and cognitive sovereignty. Ultra Unlimited. https://www.ultra-unlimited.com/blog/quantum-enhanced-holographic-defense-architecture
Integrated Foundational & Doctrinal Works Used in Production
Kallenborn, Z. (2023). The dawn of seventh-generation warfare: Autonomous systems, synthetic cognition, and moral deterrence. Parameters, 53(2), 45–58. https://press.armywarcollege.edu/parameters
NATO Cooperative Cyber Defence Centre of Excellence (CCDCOE). (2024). Cognitive warfare and the future operational environment: NATO concept note 7G. Tallinn, Estonia.
Scharre, P. (2018). Army of none: Autonomous weapons and the future of war. W. W. Norton & Company.
National Institute of Standards and Technology (NIST). (2022). NIST announces first four quantum-resistant cryptographic algorithms. https://www.nist.gov/news-events/news/2022/07/nist-announces-first-four-quantum-resistant-cryptographic-algorithms
UNESCO. (2021). Recommendation on the ethics of artificial intelligence. https://unesdoc.unesco.org/ark:/48223/pf0000381137
Ienca, M., & Andorno, R. (2017). Towards new human rights in the age of neuroscience and neurotechnology. Life Sciences, Society and Policy, 13(1), 5. https://doi.org/10.1186/s40504-017-0050-1
Heinz, J. D. (2025d). Spectral-Fractal-Medical: The Compassion Protocol. Ultra Unlimited. https://www.ultra-unlimited.com/blog/spectral-fractal-medical-the-compassion-protocol
Heinz, J. D. (2025e). The Compassion Protocol: Legal, ethical and economic foundations for cognitive sovereignty. Ultra Unlimited. https://www.ultra-unlimited.com/blog/the-compassion-protocol-legal-ethical-and-economic-foundations-for-cognitive-sovereignty
ABOUT THE AUTHORS
This research represents collaborative effort across cybersecurity practitioners, cognitive scientists, and infrastructure operators committed to advancing post-ransomware defensive paradigms.
For inquiries regarding HDA pilot deployment, threat intelligence collaboration, or research partnerships:
Ultra Unlimited
www.ultra-unlimited.com
Document Version: 1.0
Publication Date: October 2025
Classification: Public Distribution
Figure 22 — Guardian of Dual Continuums: The Heart of Equilibrium
This image represents the living mediator of opposites within the Holographic Defense Architecture (HDA)—the human field through which dual systems reach harmony.
The red and blue circuits symbolize bi-hemispheric coherence: the union of analytical and emotional intelligence, logic and intuition.
His tattoos and insignia echo the Spectral–Fractal–Symbolic Intelligence (SFSI) geometry, while the armor conveys that compassion too requires discipline and protection.
Behind him, the interwoven rings mark the infinite continuity of existence, representing recursive coherence—a dynamic equilibrium maintained through awareness, not control.
The Guardian thus stands as the sentinel of lawful balance, a human algorithm of compassion-in-action.
11. Integration with Existing Frameworks
HDA aligns with established cybersecurity standards, enabling organizations to demonstrate compliance through holographic defense deployment.
NIST Cybersecurity Framework (CSF) 2.0 Alignment
Purpose: Demonstrate HDA conformance with NIST CSF 2.0 by mapping each function to its corresponding SFSI or HBL operational layer, ensuring coherence across risk, detection, response, and recovery cycles.
| CSF Function | Specific Control | HDA Component |
|---|---|---|
| IDENTIFY | ID.RA — Risk Assessment | SFSI scores provide quantitative risk metrics across spectral, fractal, and symbolic domains. |
| DETECT | DE.CM — Continuous Monitoring | SGDI temporal anomaly detection for coherence loss and covert-channel activity. |
| DETECT | DE.AE — Anomaly Analysis | CFCS behavioral divergence analysis revealing recursive attack propagation. |
| RESPOND | RS.RP — Response Planning | HBL decision branches and adaptive incident playbooks enforcing coherence recovery. |
| RESPOND | RS.AN — Analysis | Multi-Hypothesis Tracking (MHT) module for quantum-classical threat correlation. |
| RECOVER | RC.CO — Communications | SEC meaning-integrity briefings ensuring narrative alignment during post-incident recovery. |
Interpretive Summary: HDA operationalizes NIST CSF 2.0 through measurable coherence indices (SGDI, CFCS, SEC) and automated HBL response logic, transforming compliance into continuous cognitive-sovereignty assurance.
NIST SP 800-53 (Security Controls)
SI-4: System Monitoring: SFSI telemetry collection satisfies comprehensive monitoring requirement
IR-4: Incident Handling: HBL playbooks provide documented response procedures
IR-8: Incident Response Plan: HDA architecture documents constitute comprehensive IR plan
AU-6: Audit Review: SGDI/CFCS automated analysis fulfills audit log review requirement
CIS Controls v8
Control 8: Audit Log Management: SFSI telemetry architecture
Control 13: Network Monitoring: NetFlow, PCAP, DNS analysis
Control 17: Incident Response: HBL automated response + playbooks
MITRE ATT&CK Enrichment
HDA detections map to specific ATT&CK techniques:
SGDI → T1071 (Application Layer C2): Beacon timing signatures
SGDI → T1048 (Exfiltration Over Alternative Protocol): Burst pattern detection
CFCS → T1059 (Command and Scripting Interpreter): Process graph divergence
CFCS → T1055 (Process Injection): Memory manipulation patterns
SEC → T1486 (Data Encrypted for Impact): Psychological effect mitigation
Regulatory Alignment
SEC Cyber Disclosure Rules
Public companies must disclose material cybersecurity incidents within 4 business days. HDA provides evidence of 'reasonable cybersecurity governance':
Documented risk assessment: SFSI quantitative metrics
Incident response capability: HBL playbooks, tabletop exercise records
Board oversight: Executive dashboard, meaning-integrity briefing system
DORA (Digital Operational Resilience Act - EU)
Financial sector operational resilience requirements:
Article 6: ICT risk management framework → HDA architecture documentation
Article 17: Detection and response → SFSI + HBL
Article 23: Testing → Tabletop exercises, red team validation
NIS2 Directive (EU)
Network and Information Security for essential/important entities:
Article 21: Cybersecurity risk management → SFSI continuous assessment
Article 23: Incident reporting → HBL automated timeline generation
Article 24: Supervisory cooperation → SFSI standardized metrics for reporting
AlphaGrade
Activation Checkpoint
Rapid integral, holistic, diagnostic, regenerative multi-domain research and development leveraging Spectral-Fractal-Symbolic Intelligence as a universal decoding tool across quantum micro, mezzo, and macro dimensions of reality.
Spectral-Fractal-Symbolic Intelligence
SFSI operates as a universal ontological decoding mechanism, revealing coherent patterns across all scales of existence. By synthesizing spectral temporal analysis, fractal structural recognition, and symbolic meaning extraction, AlphaGrade enables unprecedented clarity in complex system diagnostics and regenerative intervention design.
Spectral
Temporal frequency analysis revealing hidden periodicities, oscillations, and timing anomalies across behavioral, biological, and quantum systems. Fourier decomposition of time-series data exposes causal rhythms invisible to event-based observation.
Fractal
Self-similar structural pattern recognition across scales. Graph topology analysis and dimensional compression metrics detect coherent organizational principles from molecular networks to social systems to cosmic structures.
Symbolic
Meaning-space entropy characterization quantifying narrative coherence, decision integrity, and semantic density. NLP-enhanced analysis of communication patterns reveals cognitive warfare vectors and trust architecture stability.
Quantum Micro • Mezzo • Macro
AlphaGrade methodology scales seamlessly across quantum, classical, and cosmic dimensions, providing unified analytical coherence from subatomic phenomena to planetary systems.
Quantum Micro
Quantum coherence diagnostics, entanglement mapping, superconducting circuit analysis, molecular dynamics optimization, nanoscale material characterization.
Mezzo
Neural network topology, organizational resilience assessment, supply chain coherence, cognitive security architecture, biosystem regeneration protocols.
Macro
Geopolitical dynamics modeling, climate system prediction, economic stability analysis, astronomical pattern recognition, civilization-scale resilience engineering.
Rapid Integral Development
Diagnostic Scan
Multi-domain telemetry collection and SFSI metric computation. Identifies spectral anomalies, fractal divergences, and symbolic entropy spikes across target system.
Ontological Mapping
Construct holographic representation of system coherence. Reveal hidden dependencies, leverage points, and intervention opportunities through dimensional cross-correlation.
Regenerative Design
Engineer targeted interventions restoring system coherence. Deploy adaptive architectures that self-stabilize across temporal, structural, and cognitive dimensions.
Continuous Evolution
Implement feedback loops for perpetual optimization. System learns from intervention outcomes, refining SFSI models and autonomous response capabilities.
Initiate AlphaGrade
Deploy ontological operations across your organization. Activate universal SFSI decoding protocols for rapid diagnostic insight and regenerative system transformation.